
Cisco Certified Support Technician (CCST) Cybersecurity Questions and Answers
Which security assessment of IT systems verifies that PII data is available, accurate, confidential, and accessible only by authorized users?
You work for a hospital that stores electronic protected health information (ePHI) in an online portal. Authorized employees can use their mobile devices to access patient ePHI.
You need to ensure that employees’ mobile devices comply with HIPAA regulations.
Which safeguard should you develop and implement?
A remote worker is visiting a branch office to attend face-to-face meetings. The worker tries to associate their company laptop with the branch wireless access point (WAP) but is unable to do so.
What is a possible cause?
Which macOS security feature encrypts the entire macOS volume?
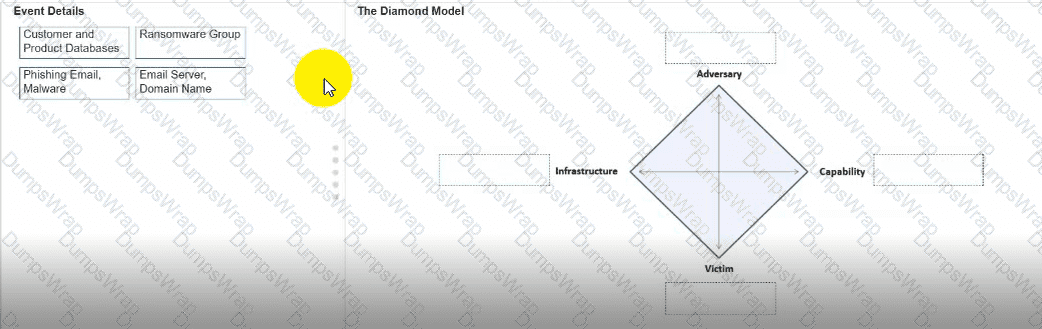
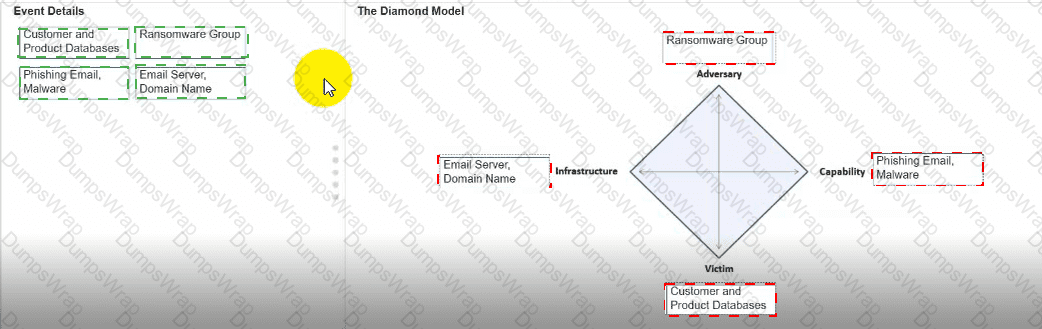
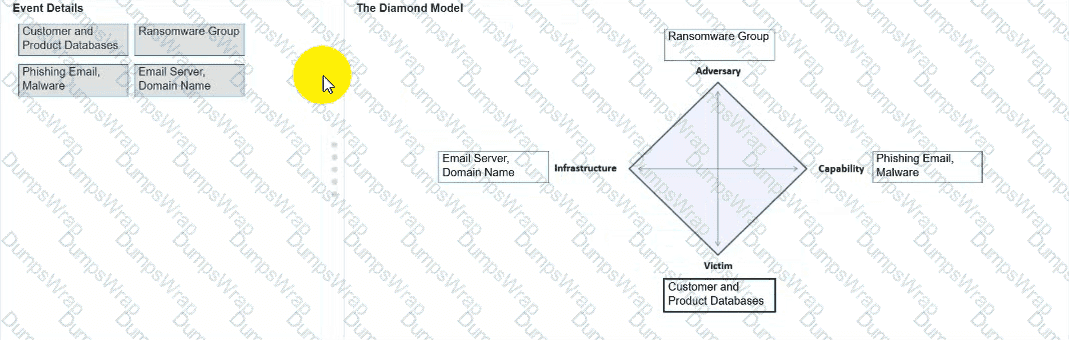
You need to diagram an intrusion event by using the Diamond Model.
Move each event detail from the list on the left to the correct location in the diagram on the right.
Note: You will receive partial credit for each correct response.
During an incident response, the security team needs to isolate a compromised server from the rest of the network but still allow forensic analysis. Which action should they take?
Which three authentication factors are valid for use in a multifactor authentication scenario? (Choose three.)
Note: You will receive partial credit for each correct selection.
You are reviewing your company’s disaster recovery plan.
Which two daily data backup actions should the plan include? (Choose 2.)
Which security measure can prevent unauthorized devices from automatically connecting to a corporate network through unused switch ports?
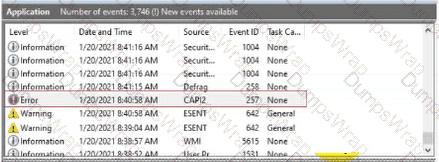
You are reviewing the Application log on a Windows computer. You see an event with an error-level message as shown.
What can you determine about the application that generated the event message?
Which wireless encryption technology requires AES to secure home wireless networks?
An administrator wants to ensure that any files downloaded from the internet are automatically scanned for malicious code before execution. Which security control should be implemented?
The company web server collects information through a form. The form is accessed by using port 80. The form content is transferred to an encrypted database for storage. You are investigating a complaint that the form content has been compromised.
What is the cause of the security breach?
You are planning to work from home. Your company requires that you connect to the company network through a VPN.
Which three critical functions do VPNs provide to remote workers? (Choose 3.)
An employee accidentally sends an email containing sensitive corporate information to an external email address.
Which type of threat does this scenario describe?
Your manager asks you to review the output of some vulnerability scans and report anything that may require escalation.
Which two findings should you report for further investigation as potential security vulnerabilities? (Choose 2.)
Which data type is protected through hard disk encryption?
What is the main purpose of a disaster recovery plan as compared to a business continuity plan?
A security assessment reveals that a system administrator accessed files outside normal working hours. The assessment identifies the commands executed and records how long the administrator was connected to the system.
Which AAA component does this represent?
Your home network seems to have slowed down considerably. You look at the home router GUI and notice that an unknown host is attached to the network.
What should you do to prevent this specific host from attaching to the network again?
