Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Questions and Answers
Refer to the exhibit.
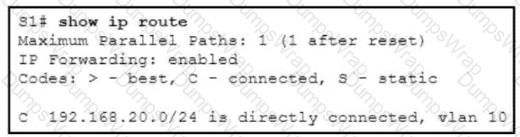
An engineer must configure a static route on the Cisco Catalyst switch to reach 192.168.10.0/24 through the 192.168.20.1 next hop. The route must use an administrative distance of 2. Which command meets the requirements?
An engineer must deploy a high-availability that includes two Cisco Secure Firewall Threat Defense devices configured as cluster. The deployment must have a mechanism that protects synchronization between cluster members Which action must the engineer take to meet the requirements?
An engineer is implementing a new Cisco Secure Firewall. The firewall must filler traffic between the three subnets:
• LAN 192.168.101.0724
• DMZ 192.168 200.0/24
• WAN 10.0.0.0/30
Which firewall mode must the engineer implement?
An engineer is setting up a remote access VPN on a Cisco FTD device and wants to define which traffic gets sent over the VPN tunnel. Which named object type in Cisco FMC must be used to accomplish this task?
A network engineer is extending a user segment through an FTD device for traffic inspection without creating another IP subnet How is this accomplished on an FTD device in routed mode?
An engineer is attempting to create a new dashboard within the Cisco FMC to have a single view with widgets from many of the other dashboards. The goal is to have a mixture of threat and security related widgets along with Cisco Firepower device health information. Which two widgets must be configured to provide this information? (Choose two).
A cisco Secure firewall Threat Defence device is configured in inline IPS mode to inspect all traffic that passes through the interfaces in the inline set. Which setting in the inline set configuration must be connected to allow traffic to pass through uninterrupted when VDB updates are being applied?
A network administrator reviews me attack risk report and notices several Low-Impact attacks. What does this type of attack indicate?
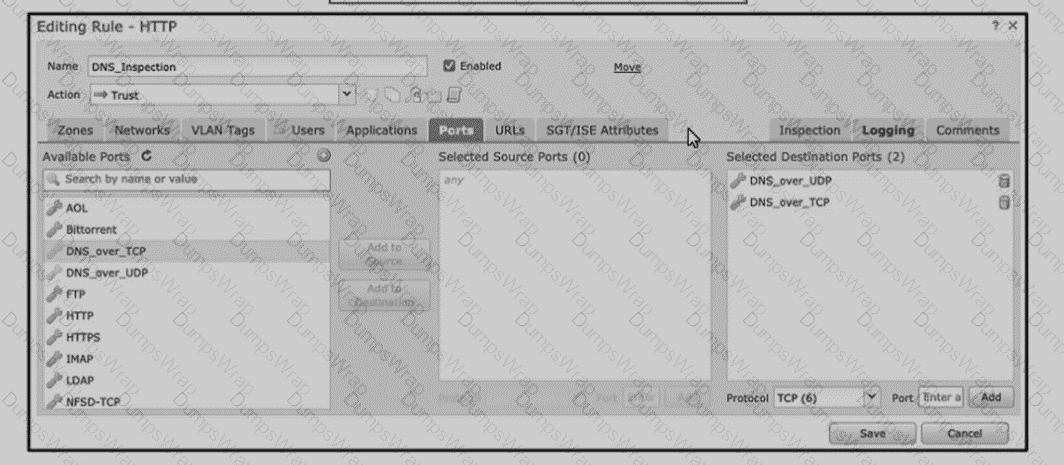
Refer to the exhibit An engineer is modifying an access control pokey to add a rule to inspect all DNS traffic that passes through the firewall After making the change and deploying thepokey they see that DNS traffic is not bang inspected by the Snort engine What is the problem?
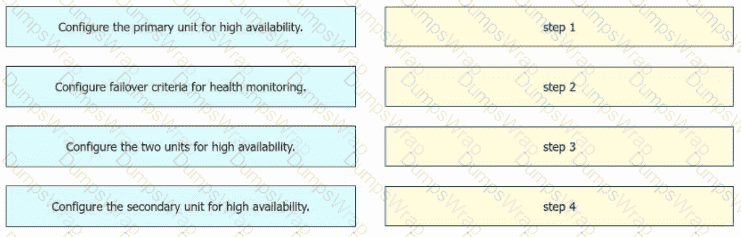
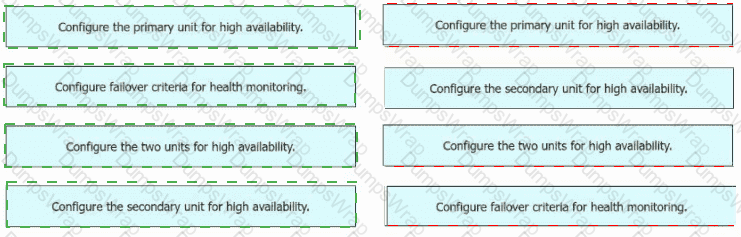
An engineer must configure high availability on two Cisco Secure Firewall Threat Defense appliances. Drag and drop the configuration steps from the left into the sequence on the right.
An engineer is setting up a new Firepower deployment and is looking at the default FMC policies to start the implementation During the initial trial phase, the organization wants to test some common Snort rules while still allowing the majority of network traffic to pass Which default policy should be used?
An engineer is configuring a new dashboard within Cisco Secure Firewall Management Center and is having trouble implementing a custom widget. When a custom analysis widget is configured which option is mandatory for the system to display the information?
A network administrator wants to configure a new Secure Firewall Threat Defense instance, which is managed by Cisco Secure Firewall Management Center, to load balance internet-bound traffic across multiple zones. Secure Firewall is connected to upstream ISP devices in multiple Zones. Which action must be taken to meet the requirement?
A network engineer detects a connectivity issue between Cisco Secure Firewall Management Center and Cisco Secure Firewall Threat Defense. Initial troubleshooting indicates that heartbeats and events are not being received. The engineer re-establishes the secure channels between both peers. Which two commands must the engineer run to resolve the issue? (Choose two.)
An engineer must configure the firewall to monitor traffic within a single subnet without increasing the hop count of that traffic. How would the engineer achieve this?
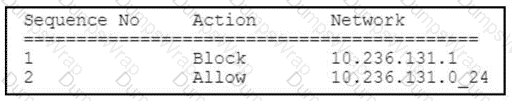
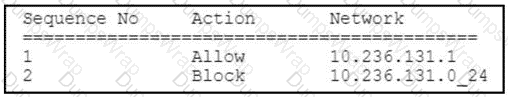
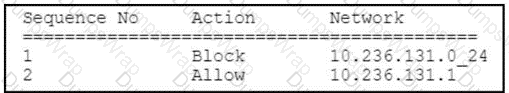
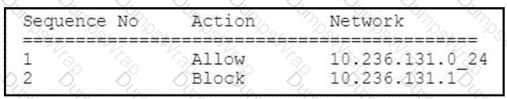
A security engineer must create an access list object in Cisco Secure Firewall Management Center to allow traffic to IP address 10.236.131.1 but block traffic to IP address 10.236.131.0/24. Which access control entries must the engineer create?
A)
B)
C)
D)
An engineer defines a new rule while configuring an Access Control Policy. After deploying the policy, the rule is not working as expected and the hit counters associated with the rule are showing zero. What is causing this error?
Which two routing options are valid with Cisco FTD? (Choose Two)
An engineer currently has a Cisco FTD device registered to the Cisco FMC and is assigned the address of 10 10.50.12. The organization is upgrading the addressing schemes and there is a requirement to convert the addresses to a format that provides an adequate amount of addresses on the network What should the engineer do to ensure that the new addressing takes effect and can be used for the Cisco FTD to Cisco FMC connection?
An engineer must investigate a connectivity issue from an endpoint behind a Cisco FTD device and a public DNS server. The endpoint cannot perform name resolution queries. Which action must the engineer perform to troubleshoot the issue by simulating real DNS traffic on the Cisco FTD while verifying the Snarl verdict?
An organization is implementing Cisco FTD using transparent mode in the network. Which rule in the default Access Control Policy ensures that this deployment does not create a loop in the network?
The administrator notices that there is malware present with an .exe extension and needs to verify if any of the systems on the network are running the executable file. What must be configured within Cisco AMP for Endpoints to show this data?
A network engineer wants to disable the HTTP response page and interactive blocking of the entire access control policy in Cisco Secure Firewall Management Center. What must be
selected in Block Response Page and Interactive Block Response Page?
What is the RTC workflow when the infected endpoint is identified?
An engineer is configuring a Cisco Secure Firewall Threat Defense device to operate in transparent mode between two switch stacks. VLAN 10 is used for in-band management on both switch stacks. Which two actions are required on the device to inspect traffic between the switch stacks without interrupting network traffic? (Choose two.)
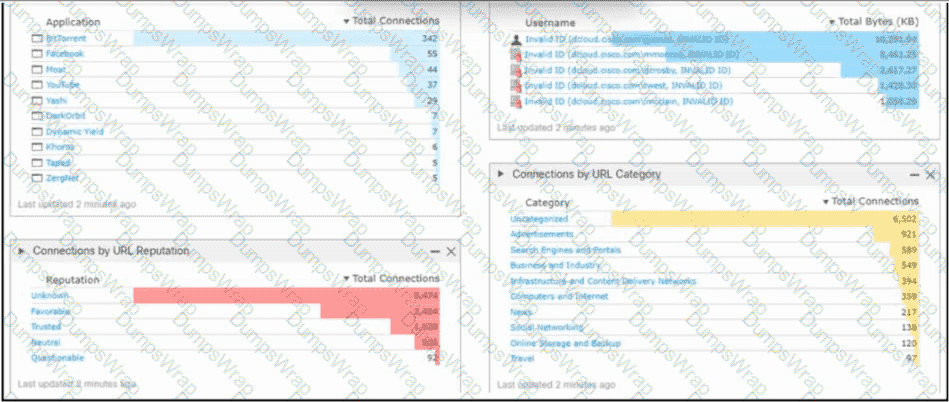
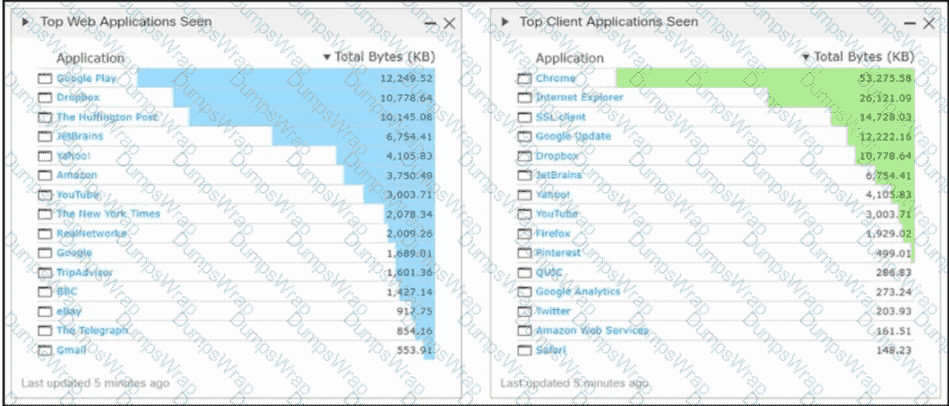
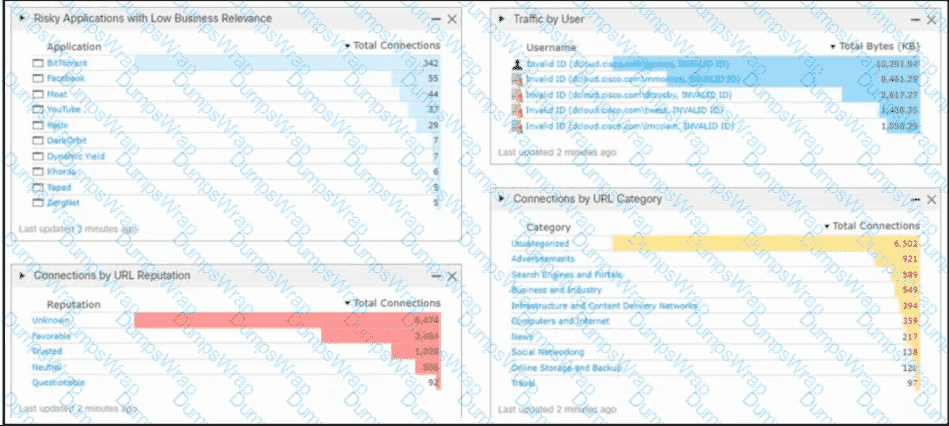
Refer to the exhibit. An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must be taken by the user to decrease the risk of data loss?
A network administrator observes an attempted attack from a specific IP address in Cisco Secure Firewall Management Center. Which Cisco security tool can be used directly from the Secure Firewall Management Center web interface to obtain additional information about the IP address?
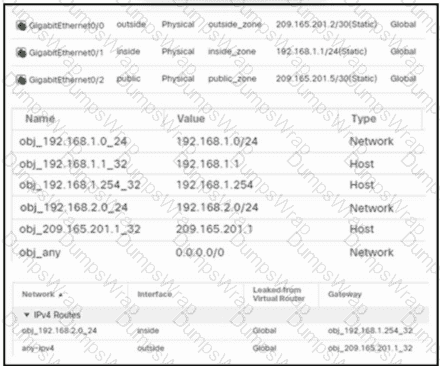
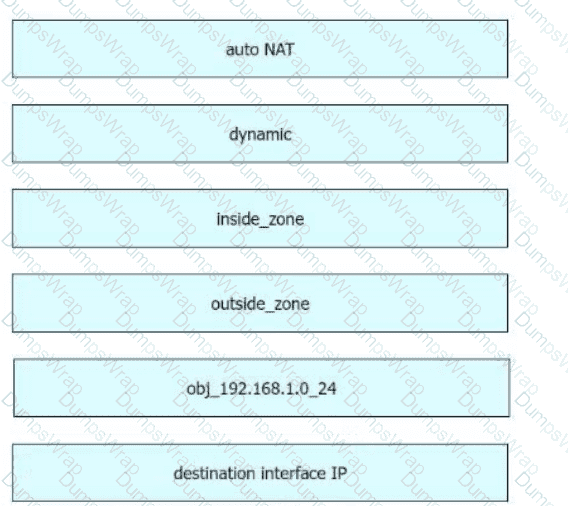
Refer to the exhibit. An engineer configures a NAT rule allowing clients to use the internet only if clients are located on the directly connected internal network. Dynamic auto PAT must be configured. Drag and drop the NAT rules from the left onto the corresponding targets on the right. Not all options are used.
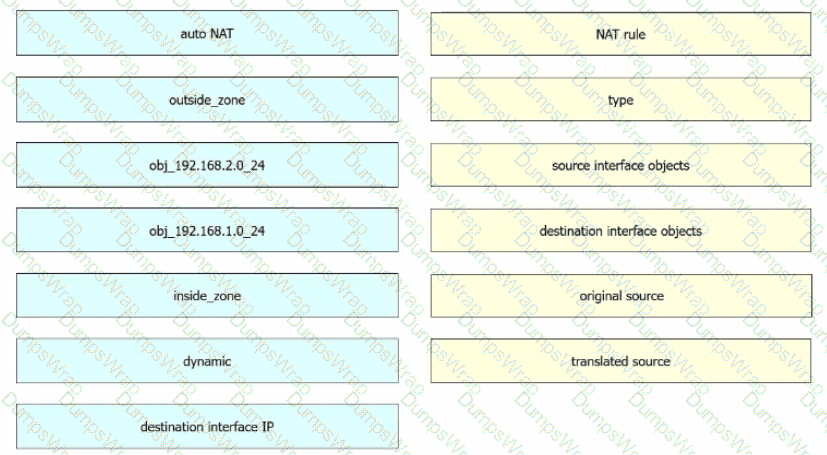

 A screenshot of a computer AI-generated content may be incorrect.
When creating a report template, how can the results be limited to show only the activity of a specific subnet?
An engineer must deploy a Cisco FTD device. Management wants to examine traffic without requiring network changes that will disrupt end users. Corporate security policy requires the separation of management traffic from data traffic and the use of SSH over Telnet for remote administration. How must the device be deployed to meet these requirements?
Which CLI command is used to control special handling of ClientHello messages?
A VPN administrator converted an instance of Cisco Secure Firewall Threat Defense, which is managed by Cisco Secure Firewall Management Center, from using LDAP to LDAPS for
remote access VPN authentication. Which certificate must be added to allow for remote users to authenticate over the VPN?
In a Cisco AMP for Networks deployment, which disposition is returned if the cloud cannot be reached?
A network engineer must configure an existing firewall to have a NAT configuration. The now configuration must support more than two interlaces per context. The firewall has previously boon operating transparent mode. The Cisco Secure Firewall Throat Defense (FTD) device has been deregistered from Cisco Secure Firewall Management Center (FMC). Which set of configuration actions must the network engineer take next to meet the requirements?
A network engineer must provide a high-level statistical summary of a Cisco Secure Firewall Threat Defense device. The organization is approaching its peak season, so network downtime must be minimized. Which type of report must the network engineer use?
Which command is run on an FTD unit to associate the unit to an FMC manager that is at IP address 10.0.0.10, and that has the registration key Cisco123?
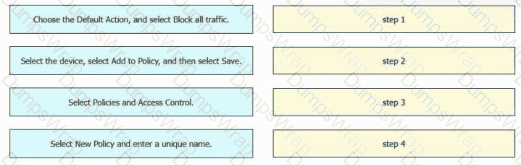
An engineer must create a basic access control policy in the Cisco Secure Firewall Management Center to block all traffic by default. Drag and drop the configuration actions from the left into sequence on the right.

An organization has a compliancy requirement to protect servers from clients, however, the clients and servers all reside on the same Layer 3 network Without readdressing IP subnets for clients or servers, how is segmentation achieved?
Refer to the exhibit.
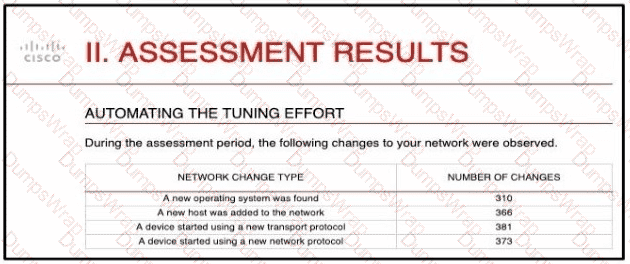
And engineer is analyzing the Attacks Risk Report and finds that there are over 300 instances of new operating systems being seen on the network How is the Firepower configuration updated to protect these new operating systems?
A network engineer must monitor threat events from the console of Cisco Secure Firewall Management Center. The engineer integrates the Cisco Secure Firewall Malware Defense in Secure Firewall Management Center. Which action must the engineer take next?
With Cisco FTD software, which interface mode must be configured to passively receive traffic that passes through the appliance?
A network administrator must create an EtherChannel Interface on a new Cisco Firepower 9300 appliance registered with an FMC tor high availability. Where must the administrator create the EtherChannel interface?
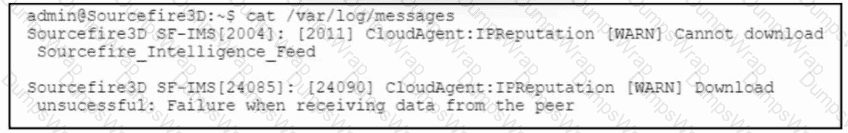
Refer to the exhibit. A Cisco Secure Firewall Management Center, 7.0 device fails to receive intelligence feed updates. The Cisco Secure Firewall Management Center is configured to use a proxy server that performs SSL inspection. Which action allows the Cisco Secure Firewall Management Center device to download the intelligence feed updates?
An engineer must deploy URL filtering in Cisco Secure Firewall Management Center Version 7.0. The engineer is configuring a URL condition for an access control rule to filter websites that display bad behavior or are malicious or undesirable. Which reputation level must be configured?
An engineer wants to change an existing transparent Cisco FTD to routed mode.
The device controls traffic between two network segments. Which action is mandatory to allow hosts to reestablish communication between these two segments after the change?
In a multi-tennent deployment where multiple domains are in use. which update should be applied outside of the Global Domain?
A network administrator is reviewing a weekly scheduled attacks risk report and notices a host that is flagged for an impact 2 attack. Where should the administrator look within Cisco FMC to find out more relevant information about this host and attack?
An engineer must investigate a connectivity issue and decides to use the packet capture feature on Cisco FTD. The goal is to see the real packet going through the Cisco FTD device and see the Snort detection actions as a part of the output. After the capture-traffic command is issued, only the packets are displayed. Which action resolves this issue?
An engineer Is configuring a Cisco FTD device to place on the Finance VLAN to provide additional protection tor company financial data. The device must be deployed without requiring any changes on the end user workstations, which currently use DHCP lo obtain an IP address. How must the engineer deploy the device to meet this requirement?
An engineer must export a packet capture from Cisco Secure Firewall Management Center to assist in troubleshooting an issue an a Secure Firewall Threat Defense device. When the engineer navigates to URL for Secure Firewall Management Center at:
.. < FMC IP > /capture/CAP/pcap/sample.pcap
An engineer receives a 403: Forbidden error instead of being provided with the PCAP file. Which action resolves the issue?
An organization is configuring a new Cisco Firepower High Availability deployment. Which actionmust be taken to ensure that failover is as seamless as possible to end users?
An engainermust add DNS-specific rules to me Cisco FTD intrusion policy. The engineer wants to use the rules currently in the Cisco FTD Snort database that are not already enabled but does not want to enable more than are needed. Which action meets these requirements?
Encrypted Visibility Engine (EVE) is enabled under which lab on an access control policy in Cisco Secure Firewall Management Centre?
Remote users who connect via Cisco AnyConnect to the corporate network behind a Cisco FTD device report that they get no audio when calling between remote users using their softphones. These same users can call internal users on the corporate network without any issues. What is the cause of this issue?
A network administrator configured an access control rule named WEB05405_SRV06798_ALLOW that allows any source on the Internet to reach the public IP address of a web server on port 8080. The administrator also configured a NAT policy that translates the public IP address to the internal web server IP address. During testing, the web server is not reachable from the Internet on port 8080. Which configuration must the administrator apply to resolve the issue?
An engineer is configuring a cisco FTD appliance in IPS-only mode and needs to utilize fail-to-wire interfaces. Which interface mode should be used to meet these requirements?
An engineer is configuring Cisco Security Devices by using Cisco Secure Firewall Management Center. Which configuration command must be run to compare the CA certificate bundle on the local system to the latest CA bundle from the Cisco server?
A security engineer found a suspicious file from an employee email address and is trying to upload it for analysis, however the upload is failing. The last registration status is still active. What is the cause for this issue?
Which limitation applies to Cisco Firepower Management Center dashboards in a multidomain environment?
A network administrator notices that inspection has been interrupted on all non-managed interfaces of a device. What is the cause of this?
Which component simplifies incident investigation with Cisco Threat Response?
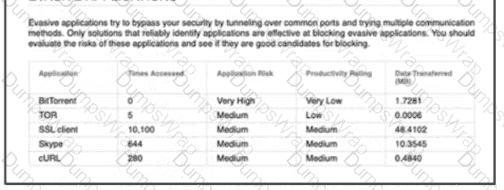
Refertothe exhibit. An engineer is analyzing a Network Risk Report from Cisco FMC. Which application must the engineer take immediate action against to prevent unauthorized network use?
A network administrator notices that remote access VPN users are not reachable from inside the network. It is determined that routing is configured correctly, however return traffic is entering the firewall but not leaving it What is the reason for this issue?
An engineer wants to connect a single IP subnet through a Cisco FTD firewall and enforce policy. There is a requirement to present the internal IP subnet to the outside as a different IP address. What must be configured to meet these requirements?
What is a benefit of implementing Integrated Routing and Bridging (IRB) on a Cisco Secure Firewall device?
A security analyst is investigating a potential network compromise. The analyst must produce a report of the suspicious activity from Cisco Secure Firewall Management Center. Which two details must be included in the report to assist the investigation? (Choose two.)
A company wants a solution to aggregate the capacity of two Cisco FTD devices to make the best use of resources such as bandwidth and connections per second. Which order of steps must be taken across the Cisco FTDs with Cisco FMC to meet this requirement?
A network administrator is configuring Snort inspection policies and is seeing failed deployment messages in Cisco FMC. What information should the administrator generate for Cisco TAC to help troubleshoot?
An organization is using a Cisco FTD and Cisco ISE to perform identity-based access controls. A network administrator is analyzing the Cisco FTD events and notices that unknown user traffic is being allowed through the firewall. How should this be addressed to block the traffic while allowing legitimate user traffic?
An engineer must configure a correlation policy in Cisco Secure Firewall Management Center to detect when an IP address from an internal network communicates with a known malicious host. Connections made by the internal IP addresses must be tracked, and an external dynamic list must be used for the condition. Which type of event must the engineer configure on the correlation policy?
Which Cisco Firepower Threat Defense, which two interface settings are required when configuring a routed interface? (Choose two.)
An engineer has been tasked with using Cisco FMC to determine if files being sent through the network are malware. Which two configuration tasks must be performed to achieve this file lookup? (Choose two).
What is the advantage of having Cisco Firepower devices send events to Cisco Threat Response via the security services exchange portal directly as opposed to using syslog?
Which two deployment types support high availability? (Choose two.)
A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?
A network engineer wants to add a third-party threat feed into the Cisco FMC for enhanced threat detectionWhich action should be taken to accomplish this goal?
When do you need the file-size command option during troubleshooting with packet capture?
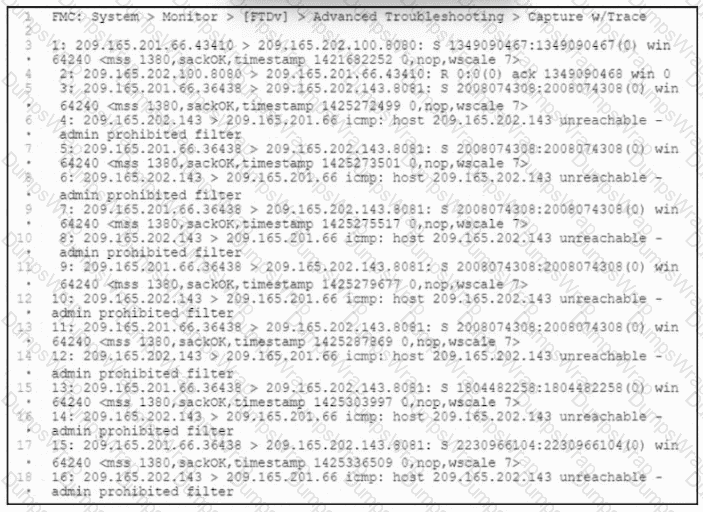
Refer to the exhibit. Users attempt to connect to numerous external resources on various TCP ports. If the users mistype the port, their connection closes immediately, and it takes more than one minute before the connection is torn down. An engineer manages to capture both types of connections as shown in the exhibit. What must the engineer configure to lower the timeout values for the second group of connections and resolve the user issues?
Which Cisco Rapid Threat Containment mitigation action is enabled by integrating pxGrid Adaptive Network Control with Cisco ISE and Cisco Secure Firewall Management Center?
An engineer wants to convert a Cisco Secure Firewall Threat Defense device that is currently managed by Cisco Secure Firewall Management Center from routed mode to transparent mode. Which CLI command must the engineer execute first to perform this conversion?
A network administrator cannot select the link to be used for failover when configuring an active/passive HA Cisco FTD pair.
Which configuration must be changed before setting up the high availability pair?
A connectivity issue is occurring between a client and a server which are communicating through a Cisco Firepower device While troubleshooting, a network administrator sees that traffic is reaching the server, but the client is not getting a response Which step must be taken to resolve this issue without initiating traffic from the client?
Which object type supports object overrides?
What is a result of enabling Cisco FTD clustering?
What is a behavior of a Cisco FMC database purge?
How does Cisco Secure Cloud Analytics handle information about network traffic?
In which two ways do access control policies operate on a Cisco Firepower system? (Choose two.)
A security engineer must create a Network Operations Center dashboard to display detailed information about the events collected by Secure Firewall Management Center. A Custom Analysis widget must be configured to display how many intrusion events of each type occurred by using the Intrusion Events table, with the data aggregated by Event Count. Which field must be configured to create the widget?
Which two statements about bridge-group interfaces in Cisco FTD are true? (Choose two.)
An engineer must deploy a high-availability pair that includes two Cisco Secure Firewall Threat Defense devices. The deployment must provide a mechanism that protects synchronization traffic between the members. Which action must the engineer take?
What is the result of specifying of QoS rule that has a rate limit that is greater than the maximum throughput of an interface?
An administrator needs to configure Cisco FMC to send a notification email when a data transfer larger than 10 MB is initiated from an internal host outside of standard business hours. Which Cisco FMC feature must be configured to accomplish this task?
A network administrator is configuring an FTD in transparent mode. A bridge group is set up and an access policy has been set up to allow all IP traffic. Traffic is not passing through the FTD. What additional configuration is needed?
A user within an organization opened a malicious file on a workstation which in turn caused a ransomware attack on the network. What should be configured within the Cisco FMC to ensure the file is tested for viruses on a sandbox system?
With Cisco Firepower Threat Defense software, which interface mode must be configured to passively receive traffic that passes through the appliance?
An engineer is configuring a file policy on a Cisco Secure Firewall Management Center appliance. Files with an Unknown disposition must be analyzed by Cisco Secure Malware Analytics. What must be configured on the Secure Firewall Management Center appliance?
A network administrator discovers that a user connected to a file server and downloaded a malware file. The Cisc FMC generated an alert for the malware event, however the user still remained connected. Which Cisco APM file rule action within the Cisco FMC must be set to resolve this issue?
An engineer has been tasked with using Cisco FMC to determine if files being sent through the network are malware. Which two configuration takes must be performed to achieve this file lookup? (Choose two.)
An engineer must replace a Cisco Secure Firewall high-availability device due to a failure. When the replacement device arrives, the engineer must separate the high-availability pair from Cisco Secure Firewall Management Center Which action must the engineer take first to restore high availability?
Which firewall mode is Cisco Secure Firewall Threat Defense in when two physical interfaces are assigned to a named BVI?
An organization has noticed that malware was downloaded from a website that does not currently have a known bad reputation. How will this issue be addresses globally in the quickest way possible and with the least amount of impact?
A network administrator is configuring a Cisco Secure Firewall Threat Defense device managed by Cisco Secure Firewall Management Center to exchange routing information with an upstream BGP router. The administrator must verify which networks the device is advertising to the upstream router. Which action must the administrator take?
Refer to the exhibit.
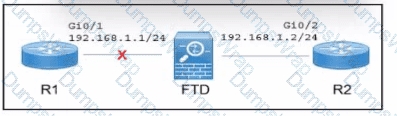
A Cisco Secure Firewall Threat Defense (FTD) device is deployed in inline mode with an inline set. The network engineer wants router R2 to remove the directly connected route M 68.1.0/24 from its routing table when the cable between routed R1 and the Secure FTD device Is disconnected. Which action must the engineer take?
1
Which action must be taken to configure an isolated bridge group for IRB mode on a Cisco Secure Firewall device?
An administrator must fix a network problem whereby traffic from the inside network to a webserver is not getting through an instance of Cisco Secure Firewall Threat Defense. Which command must the administrator use to capture packets to the webserver that are dropped by Secure Firewall Throat Defense and resold the issue?
Which CLI command is used to generate firewall debug messages on a Cisco Firepower?
Which interface mode on the firewall must be deployed on a Cisco Secure Firewall Threat Defense when implementing an IPS using a SPAN port for traffic monitoring?
An organization recently implemented a transparent Cisco FTD in their network.
They must ensure that the device does not respond to insecure SSL/TLS protocols.
Which action accomplishes the task?
What acts as the remediation module for Rapid Threat Containment within Cisco Secure Firewall Management Center?
An engineer is implementing Cisco FTD in the network and is determining which Firepower mode to use. The organization needs to have multiple virtual Firepower devices working separately inside of the FTD appliance to provide traffic segmentation Which deployment mode should be configured in the Cisco Firepower Management Console to support these requirements?
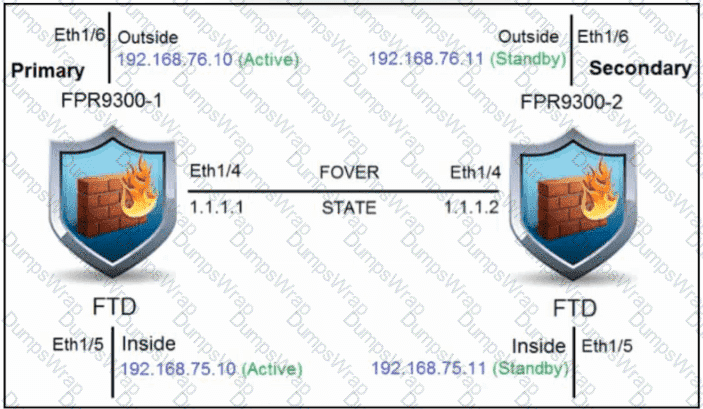
Refer to the exhibit. An engineer is configuring a high-availability solution that has the hardware devices and software versions:
two Cisco Secure Firewall 9300 Security Appliances with FXOS SW 2.0(1.23)
software Cisco Secure Firewall Threat Defense 6.0.1.1 (build 1023) on both appliances
one Cisco Secure Firewall Management Center with SW 6.0.1.1 (build 1023)
Which condition must be met to complete the high-availability configuration?
Which two statements about deleting and re-adding a device to Cisco FMC are true? (Choose two.)
An engineer is troubleshooting a device that cannot connect to a web server. The connection is initiated from the Cisco FTD inside interface and attempting to reach 10.0.1.100 over the non-standard port of 9443 The host the engineer is attempting the connection from is at the IP address of 10.20.10.20. In order to determine what is happening to the packets on the network, the engineer decides to use the FTD packet capture tool Which capture configuration should be used to gather the information needed to troubleshoot this issue?
A)
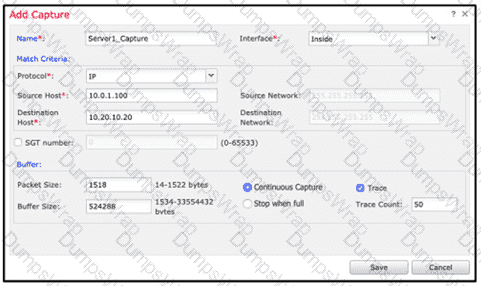
B)
C)
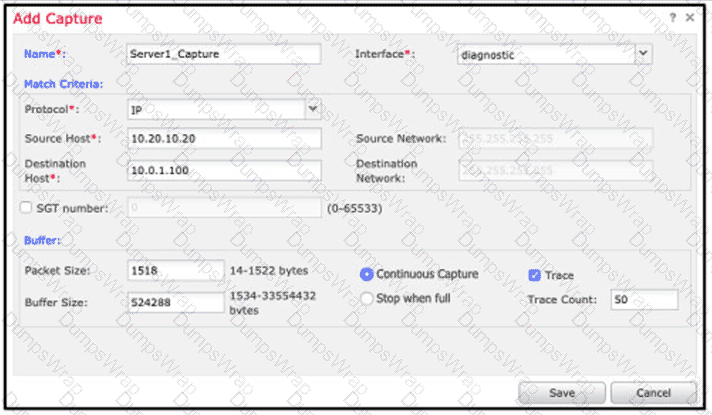
D)
A security analyst must provide detailed statics about high-bandwidth applications on a Cisco Secure Firewall Threat Defense device. The organization is approaching its peak season, so network downtime must be minimized. Which report template must the security analyst use?
An engineer must configure an inline set on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. The inline set must make a copy of each packet before analyzing the packet and block any connections that do not complete the three-way handshake. These configurations have been performed already:
Select and enable the interfaces that will be added to the inline set.
Configure the speed and duplex.
Configure the inline set and add the interfaces to the inline set.
Which action completes the task?
A security engineer is adding three Cisco FTD devices to a Cisco FMC. Two of the devices have successfully registered to the Cisco FMC. The device that is unable to register is located behind a router that translates all outbound traffic to the router ' s WAN IP address. Which two steps are required for this device to register to the Cisco FMC? (Choose two.)
An administrator is configuring a new report template off. of a saved search within Cisco Secure Firewall Management Centre. The goal is to use the malware analysis report template, but use a different type saved search as the basis. The report is not working. What must be considered when configuring this report template?
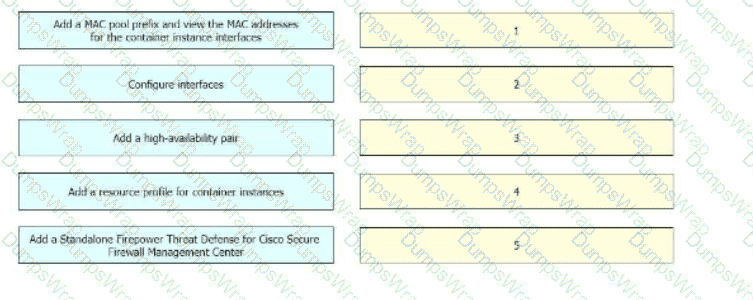
A network engineer is deploying a Cisco Firepower 4100 appliance and must configure a multi-instance environment for high availability. Drag and drop me actions from the left into sequence on the right far this configuration.

Which connector is used to integrate Cisco ISE with Cisco FMC for Rapid Threat Containment?
An administrator is optimizing the Cisco FTD rules to improve network performance, and wants to bypass inspection for certain traffic types to reduce the load on the Cisco FTD. Which policy must be configured to accomplish this goal?
Which command is typed at the CLI on the primary Cisco FTD unit to temporarily stop running high- availability?
Cisco Security Analytics and Logging SaaS licenses come with how many days of data retention by default?
A network engineer is logged into the Cisco AMP for Endpoints console and sees a malicious verdict for an identified SHA-256 hash. Which configuration is needed to mitigate this threat?
A network engineer must configure the cabling between a Cisco Secure Firewall Threat Defense appliance and a network so the Secure Firewall Threat Defense appliance performs inline to analyze and tune generated intrusion events before going live. Which Secure Firewall Threat Defense interface mode must the engineer use?
An engineer is troubleshooting application failures through a FTD deployment. While using the FMC CLI. it has been determined that the traffic in question is not matching the desired policy. What should be done to correct this?
A network engineer is tasked with minimising traffic interruption during peak traffic limes. When the SNORT inspection engine is overwhelmed, what must be configured to alleviate this issue?
A network administrator is migrating from a Cisco ASA to a Cisco FTD.
EIGRP is configured on the Cisco ASA but it is not available in the Cisco FMC.
Which action must the administrator take to enable this feature on the Cisco FTD?
What is the role of realms in the Cisco ISE and Cisco Secure Firewall Management Center integration?
An administrator is adding a new URL-based category feed to the Cisco FMC for use within the policies. The intelligence source does not use STIX. but instead uses a .txt file format. Which action ensures that regular updates are provided?
Which CLI command is used to control special handling of clientHello messages?
What are the minimum requirements to deploy a managed device inline?
An engineer is configuring a Cisco Secure Firewall Threat Defence device managed by Cisco Secure Firewall Management Centre. The device must have SSH enabled and the accessible from the inside interface for remote administration. Which type of policy must the engineer configure to accomplish this?
An organization does not want to use the default Cisco Firepower block page when blocking HTTP traffic. The organization wants to include information about its policies and procedures to help educate the users whenever a block occurs. Which two steps must be taken to meet these requirements? (Choose two.)