Weekend Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: w75best

Fortinet NSE5_FSW_AD-7.6 Dumps

Fortinet NSE 5 - FortiSwitch 7.6 Administrator Questions and Answers

Question 1

Refer to the exhibits.

as

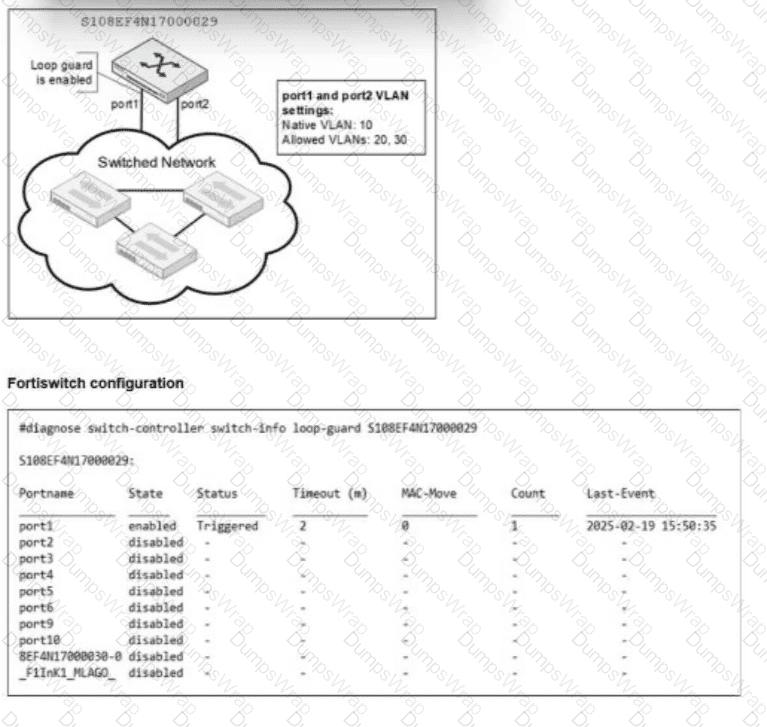
You are reviewing a FortiSwitch configuration where port1 and port2 are connected to a switched network. Loop guard is enabled on port1.

The CLI output shows that the port1 status is triggered due to loop guard. Which two conditions could have caused this shutdown? (Choose two.)

Options:

A.

A loop guard frame sent from port1 is received on port2.

B.

A loop guard frame sent from port1 is received back on port1.

C.

Loop guard is triggered because port2 did not send any bridge protocol data units (BPDU).

D.

Loop guard is triggered because the port detected excessive traffic.

Question 2

Refer to the exhibit.

as

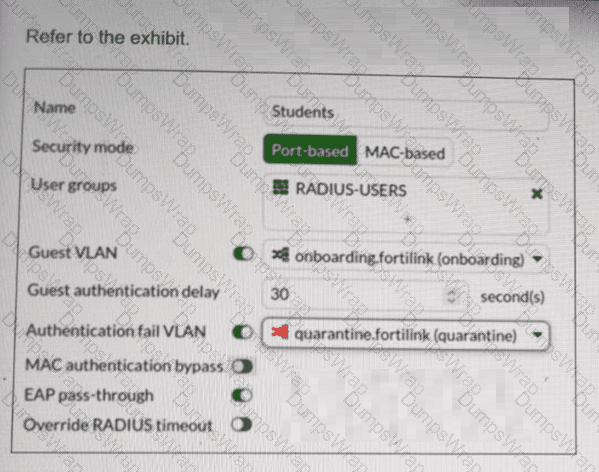
FortiSwitch 802.1X port security configuration is shown. A user connects their laptop to the port and attempts to authenticate using 802.1X, but enters the wrong credentials multiple times. What will the result to the device be? (Choose one answer)

Options:

A.

The device will be placed into the VLAN quarantine.

B.

The port will shut down for security reasons.

C.

The device will be placed into the VLAN onboarding.

D.

The device will be assigned to the default management VLAN.

Question 3

What feature can network administrators use to segment network operations and the administration of managed FortiSwitch devices on FortiGate?

Options:

A.

FortiGate multi-tenancy

B.

Multi-chassis link aggregation trunk

C.

FortiGate clustering protocol

D.

FortiLink split interface

Question 4

Exhibit.

The exhibit shows the current status of the ports on the managed FortiSwitch.

Access-1.

Why would FortiGate display a serial number in the Native VLAN column associated with the port23 entry?

Options:

A.

Port23 is a member of a trunk that uses the Access-1 FortiSwitch senal number as the name of the trunk.

B.

Port23 is configured as the dedicated management interface.

C.

A standalone switch with the showm serial number is connected on por123.

D.

Ports connect to adjacent FortiSwitch devices will show their.serial number as the na-tive VLAN

Question 5

How does FortiGate handle configuration of flow tracking sampling if you export the settings to a managed FortiSwitch stack with sampling mode set to perimeter is true?

Options:

A.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces.

B.

FortiGate configures FortiSwitch to perform ingress sampling on all switch interfaces, except ICL and ISL interfaces.

C.

FortiGate configures and enables flow sampling on FortiSwitch but does not change existing sampling settings of interfaces.

D.

FortiGate configures and enables egress sampling on all management interfaces.

Question 6

Which two statements about VLAN assignments on FortiSwitch ports are true? (Choose two.)

Options:

A.

Configure a native VLAN on the FortiLink

B.

Assign an IP address and subnet mask to FortiSwitch VLANs

C.

Only assign one native VLAN on a port

D.

Assign untagged VLANs using FortiGate CLI

Question 7

Which two statements about DHCP snooping enabled on a FortiSwitch VLAN are true? (Choose two.)

Options:

A.

Enabling DHCP snooping on a FortiSwitch VLAN ensures requests and replies are seen by all DHCP servers.

B.

switch-controller-dhcp-snooping-verify-mac verifies the destination MAC address to protect against DHCP exhaustion attacks.

C.

By default, all FortiSwitch ports are set to forward client DHCP requests to untrusted ports.

D.

Settings related to DHCP option 82 are only configurable through the CLI

Question 8

Which statement about the quarantine VLAN on FortiSwitch is true?

Options:

A.

Quarantine VLAN has no DHCP server

B.

Users who fail 802.1X authentication can be placed on the quarantine VLAN.

C.

It is only used for quarantined devices if global setting is set to quarantine by VLAN.

D.

FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.

Question 9

Which Ethernet frame can create Layer 2 flooding due to all bytes on the destination MAC address being set to all FF?

Options:

A.

The broadcast Ethernet frame

B.

The unicast Ethernet frame

C.

The multicast Ethernet frame

D.

The anycast Ethernet frame

Question 10

Which two requirements must be met before FortiGate can manage a FortiSwitch stack? (Choose two answers)

Options:

A.

The latest FortiOS and FortiSwitchOS versions must be running.

B.

The switch controller feature must be enabled.

C.

All existing FortiLink interfaces must be disabled.

D.

The FortiSwitchOS version must be compatible with FortiOS.

Question 11

Which statement about the IGMP snooping querier when enabled on a VLAN is true?

Options:

A.

Active multicast receiver entries are aging on each IGMP query sent on the VLAN

B.

IGMP reports on the VLAN are forwarded to all switch ports.

C.

The setting can only be enabled using the FortiSwitch CLI.

D.

All other indirectly connected switches will be unable to get IGMP multicast traffic.

Question 12

(Full question statement start from here)

How does enabling an IGMP snooping proxy on FortiSwitch help reduce the number of IGMP reports processed by the IGMP querier? (Choose one answer)

Options:

A.

By converting IGMP reports into broadcast packets to reach all VLAN members

B.

By converting IGMP traffic to unicast

C.

By suppressing duplicate IGMP reports within the VLAN

D.

By forwarding IGMP reports only when the first member joins and the last member leaves

Question 13

Refer to the exhibit.

as

The security port policy is configured as shown in the exhibit. Which behavior occurs if a device connected to the port that does not support 802.1X? (Choose one answer)

Options:

A.

The device is blocked from accessing the network.

B.

The device is placed into the onboarding VLAN.

C.

The device is placed into the quarantine VLAN.

D.

The device is assigned to the default management VLAN.

Question 14

Which QoS mechanism maps packets with specific class of service (COS) or Differentiated Services Code Point (DSCP) markings to an egress queue? (Choose one answer)

Options:

A.

Classification for ingress traffic

B.

Queuing for egress traffic

C.

Policing for ingress traffic

D.

Shaping for egress traffic

Question 15

Refer to the exhibit.

What two conclusions can be made regarding DHCP snooping configuration? (Choose two.)

Options:

A.

Maximum value to accept clients DHCP request is configured as per DHCP server range.

B.

FortiSwitch is configured to trust DHCP replies coming on FortiLink interface.

C.

DHCP clients that are trusted by DHCP snooping configured is only one.

D.

Global configuration for DHCP snooping is set to forward DHCP client requests on all ports in the VLAN.

Question 16

You are configuring VLANs on a FortiSwitch device managed by FortiGate. Which two statements accurately describe VLAN assignment requirements and behavior on FortiSwitch ports? (Choose two answers)

Options:

A.

Untagged defines the list of VLANs that are allowed on the port for both ingress and egress traffic.

B.

Untagged VLAN applies to egress traffic only.

C.

You can assign only one native VLAN on a port.

D.

VLAN assignments must be configured directly on the FortiSwitch.

Question 17

Refer to the exhibit.

as

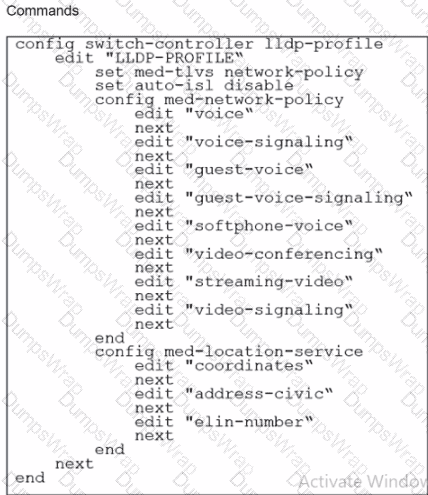
The profile shown in the exhibit is assigned to a group of managed FortiSwitch ports, and these ports are connected to endpoints which are powered by PoE.

Which configuration action can you perform on the LLDP profile to cause these endpoints to exchange PoE information and negotiate power with the managed FortiSwitch?

Options:

A.

Create new a LLDP-MED application type to define the PoE parameters.

B.

Assign a new LLDP profile to handle different LLDP-MED TLVs.

C.

Define an LLDP-MED location ID to use standard protocols for power.

D.

Add power management as part of LLDP-MED TLVs to advertise.

Question 18

What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?

Options:

A.

Use a migration tool based on python script to convert the configuration

B.

Enable the Forti-link setting on FortiSwitch before the authorization process

C.

FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.

D.

Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.

Question 19

Refer to the exhibit.

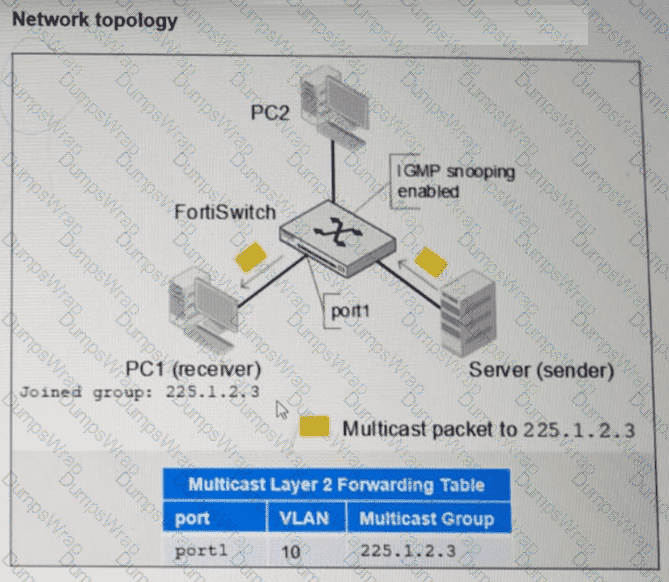
as

PC1 connected to port1 has joined multicast group 225.1.2.3 on VLAN 10 with IGMP snooping enabled. What will happen if you disable IGMP snooping on FortiSwitch? (Choose one answer)

Options:

A.

PC1 will be removed from the multicast group 225.1.2.3.

B.

The FortiSwitch will stop processing IGMP report join messages.

C.

Multicast traffic for 225.1.2.3 will be flooded to all ports.

D.

Multicast traffic will stop until a multicast receiver is detected.

Question 20

Refer to the exhibit.

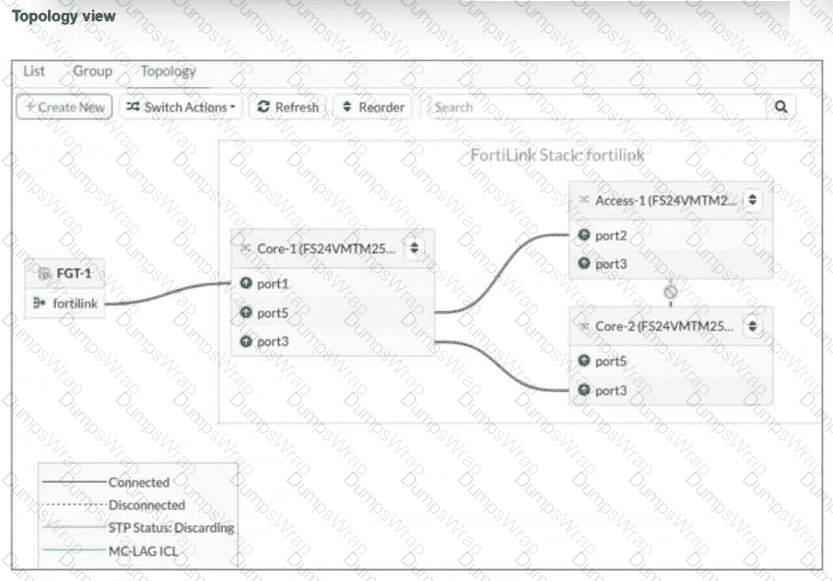
as

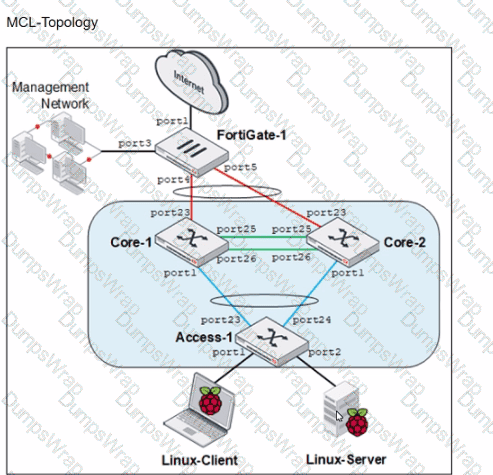
You just connected three FortiSwitch devices:Core-1,Core-2, andAccess-1. Core-1 and Core-2 both connect to Access-1 for redundancy. All switches are managed by FortiGate, which uses port4 as the FortiLink interface. After you enable the uplink ports on Core-2, you notice that port3 on Access-1 enters the Discarding STP state. What is the most likely cause of this behavior? (Choose one answer)

Options:

A.

Bridge Protocol Data Unit (BPDU) Guard is enabled, which shuts down the port after it receives BPDUs.

B.

Access-1 is not authorized by FortiGate.

C.

Core-2 has the lowest bridge priority.

D.

FortiGate is not running Spanning Tree Protocol (STP) on the FortiLink interface.

Question 21

Which LLDP-MED Type-Length-Values does FortiSwitch collect from endpoints to track network devices and determine their characteristics?

Options:

A.

Network policy

B.

Power management

C.

Location

D.

Inventory management

Question 22

Which three are valid actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose three answers)

Options:

A.

Assign the VLAN ID

B.

Quarantine devices

C.

Traffic processing

D.

Set outer VLAN tags

E.

QoS

Question 23

Which two statements about managing a FortiSwitch stack on FortiGate are true? (Choose two.)

Options:

A.

A FortiLink interface must be enabled on FortiGate.

B.

The switch controller feature must be enabled on FortiGate.

C.

Only a hardware-based FortiGate can manage a FortiSwitch stack.

D.

FortiSwitch must be operating in standalone mode before authorization.

Question 24

Refer to the diagnostic output:

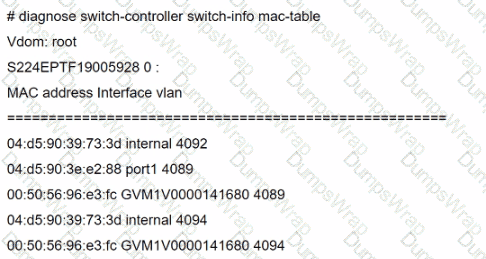
as

Two entries in the exhibit show that the same MAC address has been used in two different VLANs. Which MAC address is shown in the above output?

Options:

A.

It is a MAC address of FortiLink interface on FortiGate.

B.

It is a MAC address of a switch that accepts multiple VLANs.

C.

It is a MAC address of an upstream FortiSwitch.

D.

It is a MAC address of FortiGate in HA configuration.

Question 25

Exhibit.

port24 is the only uplink port connected to the network where access to FortiSwitch management services is possible. However, FortiSwitch is still not accessible on the management interface. Which two actions should you take to fix the issue and access FortiSwitch? (Choose two.)

Options:

A.

You must add port24 native VLAN as an allowed VLAN on internal.

B.

You must add VLAN ID 200 to the allowed VLANS on internal.

C.

You must allow VLAN ID 4094 on port24, if management traffic is tagged.

D.

You should use VLAN ID 4094 as the native VLAN on port24.

Question 26

Which packet capture method allows FortiSwitch to capture traffic on trunks and management interfaces?

Options:

A.

SPAN

B.

Sniffer profile

C.

sFlow

D.

TCP dump

Question 27

(Full question statement start from here)

How does FortiSwitch determine the route for traffic traversing its interfaces? (Choose one answer)

Options:

A.

Hardware-based routing on FortiSwitch is handled by the CPU.

B.

ASIC hardware routing can handle only dynamic routing, if supported.

C.

FortiSwitch looks up the hardware routing table and then the forwarding information base (FIB).

D.

FortiSwitch forwards all traffic to FortiGate for routing decisions.

Question 28

Which statement about 802.1X security profiles using MAC-based authentication mode is true?

Options:

A.

FortiSwitch allows connectivity to all hosts connected to a port, if one host is authenticated.

B.

FortiSwitch can grant each device a different access level based on the credentials provided

C.

FortiSwitch performs faster when using this security mode on the ports.

D.

FortiSwitch must communicate with the RADIUS server to authenticate devices

Question 29

Exhibit.

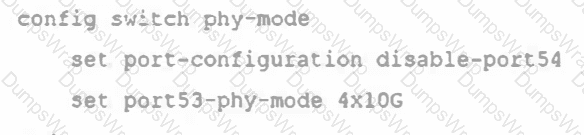
as

What conditions does a FortiSwitch need to have to successfully configure the options shown in the exhibit above? (Choose two.)

Options:

A.

The FortiSwitch model is equipped with a maximum of 54 interfaces.

B.

The CLI commands are enabling a splitpo rt into four 10Gbps interfaces.

C.

The port full speed prior the split was 100G SFP+

D.

The split port can be assigned to native VLAN

Question 30

(Full question statement start from here)

What is an advantage of using a FortiSwitch stack in managed switch mode with FortiGate when deploying VLANs? (Choose one answer)

Options:

A.

FortiGate executing the routing and FortiSwitch managing its configuration.

B.

Ensuring VLAN traffic can pass between connected switches in the stack.

C.

FortiGate no longer needing to manage any VLAN configuration.

D.

FortiGate provides visibility and control for inter-vlan traffic.

Question 31

To enhance service in emergency situations, to which LLDP-MED Type-Length-Values does Forti-Switch advertise to IP phones?

Options:

A.

Network policy

B.

Inventory management

C.

Location

D.

Power management

Question 32

How are the ' by VLAN redirect MAC address quarantine ' mode and the ' by redirect MAC address quarantine ' mode on FortiGate similar?

Options:

A.

Both modes move quarantined devices to the quarantine VLAN.

B.

Both modes require firewall policies to block inter-VLAN traffic.

C.

Both modes add quarantined device MAC addresses to the blocked firewall address group.

D.

Both modes block intra-VLAN traffic by FortiGate automatically.

Question 33

Refer to the diagnostic output:

What makes the use of the sniffer command on the FortiSwitch CLI unreliable on__port__23?

Options:

A.

The types of packets captured is limited.

B.

Just the port egress payloads are printed on CLI.

C.

Only untagged VLAN traffic can be captured.

D.

The switch port might be used as a trunk member

Question 34

Refer to the exhibit.

as

Core-1 and Access-1 are managed and authorized by FortiGate-1. which uses port4 as the FortiLink interface. After FortiGate authorizes and manages Core-2. Port1 status becomes STP discarding.

Why is port1 in the discarding state?
Options:

A.

port1 on Core-2 is discarding only management traffic.

B.

Core-1 and Core-2 do not have MCLAG configuration.

C.

Access-1 is the root bridge and can only have one root port.

D.

Core-2 has the lowest bridge priority.

Page: 1 / 11
Total 114 questions