Halloween Sale Special - 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: w75best

Fortinet NSE6_EDR_AD-7.0 Dumps

Fortinet NSE 6 - FortiEDR 7.0 Administrator Questions and Answers

Question 1

Which two Python commands are supported when using FortiEDR Connect to directly access a protected device shell? (Choose two answers)

Options:

A.

%upload_file

B.

%ipconfig_all

C.

%psexec

D.

%timestamp

Question 2

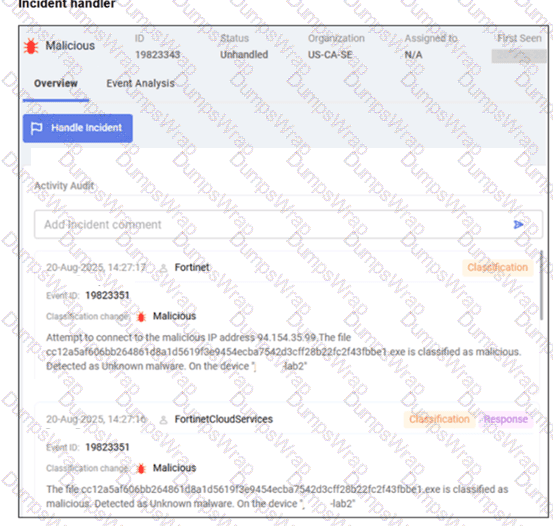
Refer to the exhibit.

as

Based on the exhibit, which two observations are true? (Choose two answers)

Options:

A.

FortiEDR has classified this as suspicious.

B.

This incident has been resolved.

C.

FCS has classified this as malicious.

D.

EDR has never encountered this malware before.

Question 3

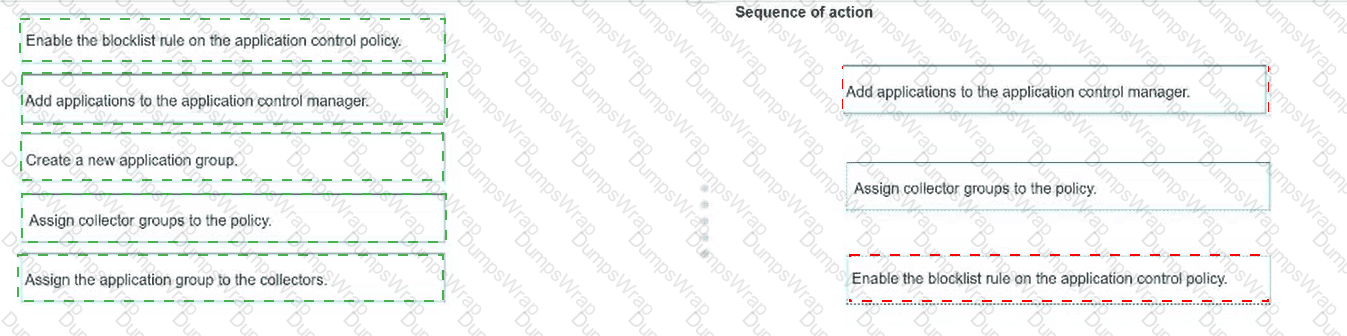
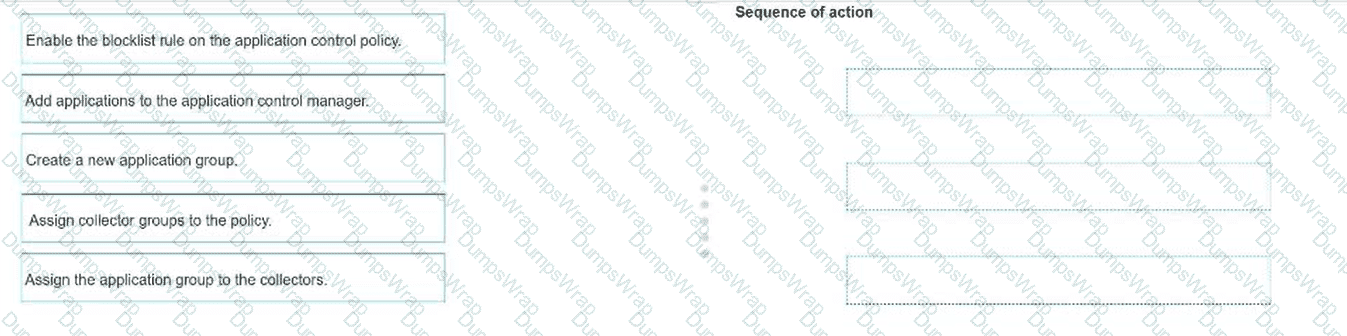
When implementing an application block policy in FortiEDR, which three actions, in order, reflect the correct operational sequence? (Choose three.)

Select an action in the left column and hold and drag it to a blank position in the column on the right. Place the three correct actions in order, starting with the first action at the top of the column. After you

place an action, you can move it again if you want to change your answer before proceeding to the next question. You must drop three actions in the work area.

Select and drag the screen divider to change the viewable area of the source and work areas.
as

Options:

Question 4

You are asked to configure a query to run every 15 minutes, automatically searching for specific registry modifications across all endpoints. Which FortiEDR feature must you configure? (Choose one answer)

Options:

A.

A communication control rule with a 15-minute delay

B.

A manual query linked to a policy override

C.

A scheduled query defined within a threat hunting profile

D.

A new playbook trigger based on the registry change event

Question 5

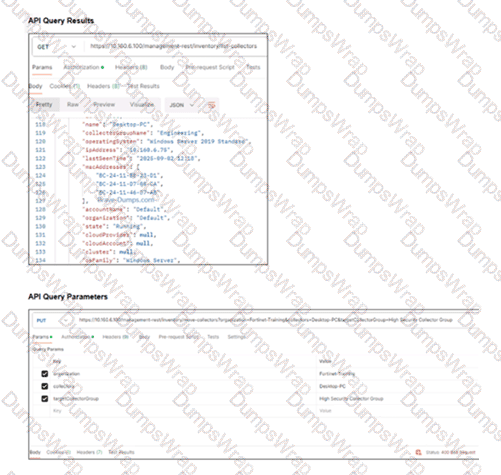
Refer to the exhibits.

as

You are attempting to move a collector into the High Security Collector Group for isolation but encounter an error in the API request as shown in the exhibit. To successfully isolate the collector, which API parameter must you correct? (Choose one answer)

Options:

A.

Set the organization parameter to Default.

B.

Update the authorization credentials in the API header.

C.

Change the HTTP method in the request from PUT to POST.

D.

Set the target collector group parameter to Engineering group.

Question 6

Which two statements correctly describe the IoT probing process on FortiEDR? (Choose two answers)

Options:

A.

Collectors running on servers are always used for IoT probing.

B.

It identifies nearby devices by retrieving details such as hostname and IP address.

C.

Only healthy collectors participate in IoT probing.

D.

It captures all traffic from neighboring devices for deep packet inspection.

Question 7

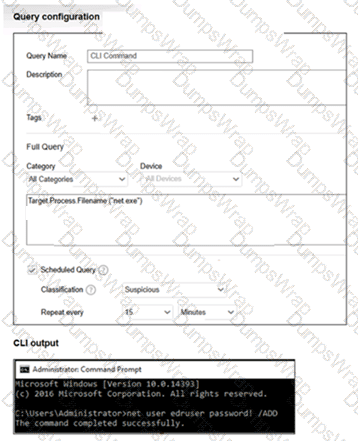
Refer to the exhibits.

as

What happens when the net user command runs on an endpoint? (Choose one answer)

Options:

A.

It triggers an immediate endpoint alert.

B.

It blocks CLI commands by default.

C.

It triggers an incident when the query matches the target process (net.exe).

D.

It triggers FortiEDR rules because the activity is not suspicious.

Question 8

A collector attempts to access a known malicious website. FortiEDR is configured for eXtended detection with FortiAnalyzer. What two roles does Fortinet Cloud Services (FCS) perform in this process? (Choose two answers)

Options:

A.

FCS sends a log record to FortiAnalyzer.

B.

FCS sends OS metadata to the FortiEDR manager.

C.

FCS correlates and analyzes the collected logs.

D.

FCS identifies if a malicious event has taken place and reports the detection incident.

Question 9

Refer to the exhibit:

as

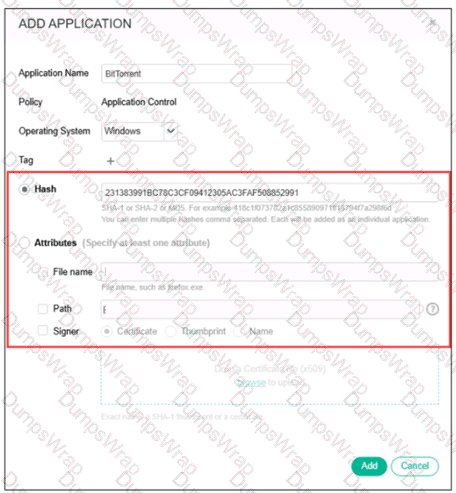
You are asked to block applications based on hash attributes. Which two factors must you consider when applying the hash value? (Choose two answers)

Options:

A.

Hashes must be line-separated.

B.

Hashes must be used with at least one attribute, such as a filename or path.

C.

Hashes must be unique to each application.

D.

Hashes must follow supported formats.

Question 10

You find third-party software on a user’s computer that does not appear in the application list on the communication control console. Which two statements are true about this situation? (Choose two answers)
Options:

A.

The application has not made any connection attempts.

B.

The application is blocked by the security policies.

C.

The application is ignored because its reputation score is acceptable to the security policy.

D.

The application is allowed in all communication control policies.

Page: 1 / 4
Total 35 questions