
IBM Guardium Data Protection v12.x Administrator – Professional Questions and Answers
Which component must be configured before you create Alert Builder email notifications?
Options:
Alert Templates
Predefined Alerts
Syslog
SMTP
Answer:
DExplanation:
"Use the Alerter and Alert Builder to create notifications. … Before you choose alerting actions, you must configure the email SMTP settings in the Alerter. … At a minimum, IP Address/Host name, port, and return email address must be specified. Select Mail from the Notification Type menu."
The Alerter is the delivery engine. The Alert Builder only defines when an alert fires and who receives it. Without a working SMTP configuration, a Mail receiver has no route to send through. Predefined alerts exist out of the box and do not need setup first. Syslog is an alternative notification type and not a prerequisite for email.
Menu paths: Protect > Database Intrusion Detection > Alerter for setup, then Alert Builder for the alert definition.
Urgent flag: A message with severity HIGH is sent with the Urgent flag set.
Receivers: Beyond users and groups, real-time email can go to the Invoker (the user whose SQL triggered the rule) and the Owner (the database owner). Both are resolved from user IDs configured through the Guardium APIs.
Alerter state: Make sure the Alerter is active after you save the SMTP settings.
Which guard-config-update option in the guard_tap.ini file configures the IP address of the Guardium system with which the S-TAP should communicate?
Options:
--set-sqlguard-ip
--set-database-ip
--set-guardium-ip
--set-tap-ip
Answer:
AExplanation:
"--set-sqlguard-ip ip/hostname: Change the address or hostname of the primary SQLGUARD appliance. Note: You can change only the primary SQLGUARD IP address."
In S-TAP terminology the Guardium collector is the "SQLGUARD" appliance, and its address is held in the SQLGUARD section of guard_tap.ini . The guard-config-update utility changes it without hand-editing the file.
Other options: --set-database-ip , --set-guardium-ip and --set-tap-ip are not options of this utility.
Related options: --set-sqlguard section1,parm=value;... modifies values in one or more SQLGUARD sections, for example secondary collectors. --show-ies lists the inspection engines.
Primary only: Only the primary collector address can be changed with --set-sqlguard-ip . Failover collectors are defined as additional SQLGUARD sections.
GIM installs: Parameters are usually managed from the GIM interface, which generates the equivalent configuration.
After a change: Restart the S-TAP service for it to reconnect to the new address. The same utility can start, stop, restart and show the status of the S-TAP.
Where are the MustGather files saved after the support must_gather command runs?
Options:
Fileserver
Healthcheck log Page
Support Information Gathering Results Page
/tmp directory in the DB server
Answer:
AExplanation:
"Running the must_gather can take several minutes. When complete, you can retrieve the file with the fileserver command. … On the fileserver, the must gather files are stored in the ../Access logs > opt-ibm-guardium-log/ ** > must_gather/ directory. Within the directory, Guardium generates the logs as .tgz files. Upload any must_gather files to ECUREP by using standard data upload. Specify the PMR number and the file to upload."
When support must_gather < issue > is run from the CLI, the output is written to the appliance's log area. You retrieve it with the fileserver command, which starts a temporary HTTP/SFTP-style file service, for example fileserver < client_IP > < minutes > .
CLI access: Log in as the cli user. You can run multiple categories as needed, such as sniffer_issues , agg_issues , cm_issues , network_issues and patch_install_issues .
GUI alternative: If you run MustGather from Manage > Maintenance > Support Information Gathering, results appear on the Support Information Results page. The default retention is 30 days.
Output location: The files stay on the Guardium appliance, not on the database server.
Encryption: MustGather output can be encrypted. The setting is under system configuration and store encrypt_must_gather .
Which statement is accurate about creating a datasource for Vulnerability Assessment?
Options:
A datasource can be created by uploading CSV files.
A datasource can only be created using CLI.
A datasource is automatically created when a database is discovered.
A datasource can only be created using the Datasource Definitions tool.
Answer:
AExplanation:
"A datasource is a database connection that is created and configured for use with Guardium applications such as Vulnerability Assessment and classifier. A datasource can be created by using the Datasource Definitions tool or by creating and uploading a CSV file by using the Customer Uploads tool in the Guardium user interface."
There are at least two supported methods, so any statement using "only" is wrong. The CSV route is useful for creating many datasources at once.
Datasource Definitions: Open Setup > Tools and Views > Datasource Definitions.
GuardAPI: Datasources can also be created with GuardAPI, so option B is incorrect. Properties such as custom properties can also be set that way.
Discovery: Auto-discovery only finds databases and reports them (Databases Discovered report). You still define the datasource with credentials. Option C is therefore wrong.
Privileges: For VA, run the Guardium-supplied script on the target database to create a suitably privileged role. Use that account in the datasource.
Enterprise deployments: Datasources must be defined on the Central Manager. Datasources created on managed units cannot be seen or used.
File Activity Monitoring is planned for a Windows server. Which installation package must be installed on the Windows server to meet the requirements?
Options:
GIM client
Exit module
S-TAP agent
FamMonitor bundle
Answer:
DExplanation:
"In Windows servers, file activity monitoring is implemented by the FamMonitor bundle. It is installed independently from S-TAP." The FamMonitor "enables monitoring and collection of audit information and policy rules, and real time alerts or blocking of suspicious users or connections on your" file servers.
Install methods: The installation package wizard, a GIM bundle after the GIM client is on the server, or the command line.
GIM: The GIM client (option A) is only the delivery mechanism. It does not perform file monitoring.
Discovery agent: For discovery and classification, the FAM discovery agent (crawler) is installed and activated on the Windows server in addition to FamMonitor.
Licensing: FAM Standard provides core functionality. FAM Advanced adds blocking.
Not S-TAP or Exit: The Windows S-TAP monitors database traffic. Exit modules apply only to Db2, Informix and Teradata on Unix and Linux.
Which component is recommended for maintaining the assessment tests and datasource definitions for Vulnerability Assessment in an Enterprise deployment?
Options:
Aggregator
Collector
Central Manager
CAS Server
Answer:
CExplanation:
"Important: In a centrally-managed environment, datasources must be defined on the central manager. Datasources that are created on managed units cannot be seen or used." Also: "Managed units that are running VA, access the central manager for definitions and content." And: "The definition of the Security Assessment itself is saved to the Central Manager. But the results are saved on the local machine."
Definitions, meaning assessment tests and datasources, are held centrally and maintained once. The assessment can then run on any managed unit or on the Central Manager itself. Results stay local to the unit that ran the assessment.
Placement: Keep the Central Manager in the same data center as its managed units. Network latency can noticeably slow retrieval of centrally defined assessment content.
Content: Guardium ships over two thousand predefined tests covering configuration parameters, privileges and other vulnerabilities. Some can be customized.
Why not the others: Aggregators and collectors consume the definitions and do not own them. A CAS server is not a Guardium component for VA definitions.
Which operating-system user must be used to install the S-TAP client on a Linux database server?
Options:
guardium
root
admin
guardadmin
Answer:
BExplanation:
"Log on to the database server using the root account. (S-TAP must always be installed by root.)" Elsewhere: "A root user that installs GIM or S-TAP needs permissions to create and delete users and groups."
The installer loads the K-TAP kernel module, places libraries in system paths and creates service accounts and groups. All of that requires root.
Disk space: Allow roughly 400–500 MB for the installation directory.
Staging: The installer is normally copied to /tmp on the database server.
Run-as setting: The --userinst and --rootinst parameters control which account the running S-TAP uses, not the account that installs it. The recommended defaults are --userinst and --root .
Shared memory: When ktap_fast_shmem is 0 and shmctl fails on permissions, running the S-TAP as root may be needed. This applies mostly to Db2 shared-memory segments readable only by the Db2 user.
Partial installs: If any stage fails, undo everything and do not leave the S-TAP partially installed.
Which role permits routine system maintenance, such as restarting services, without providing access to sensitive data or configurations?
Options:
Admin-console-only
System-admin
Maintenance
Admin
Answer:
AExplanation:
"admin-console-only: A user that is specified by this role can only access the admin console tab."
The role-to-application mapping gives this role Support access (Support Information Gathering, Support Information Results, Support Maintenance) and System Configuration. These are operational functions, and the role carries no access to reports, policies or audit data. The admin role, by contrast, "provides the default layout and access for Guardium administrators" and by default has access to all objects.
Admin Console: The Administration Console is where an operator restarts services and the portal, runs support tools and views system health. Restricting a user to this tab lets them perform maintenance without seeing monitored data.
Roles that do not exist: "System-admin" and "Maintenance" are not default or sample Guardium roles. The default roles are user, admin, accessmgr, cli, inv, datasec-exempt and review-only, plus the sample roles such as dba, infosec, audit, admin-console-only, cas and fam.
Separation of duties: The admin role and the access manager role cannot be assigned to the same user.
How frequently is the Vulnerability Assessment Database Protection Subscription (DPS) distributed?
Options:
Every six months
Quarterly basis
Monthly basis
Bi-weekly basis
Answer:
BExplanation:
"The Database Protection Subscription service (DPS) publishes updates to known vulnerabilities (known risks)." The release notes state: "Tests and groups that are added after the release of Guardium version 12.0 will be available in upcoming quarterly DPS reports." DPS files are named by quarter, for example Guardium_V11_Quarterly_2019_Q1_20190227.enc .
DPS updates the Vulnerability Assessment test library, groups and CVE-based content, and is published four times a year.
Installing: Download the latest DPS file from IBM Fix Central. Upload it through Customer Uploads, then import it. In a Central Manager environment, upload it to the Central Manager. In a standalone environment, upload it to each collector.
Checking: Run show dps for installation status. A DPS file can take a long time to install. If you restart the browser the install stops, so keep the upload window open.
Optional, but recommended: The DPS file is not mandatory. Without it, risk scores are partial, and Risk Spotter's accuracy suffers. Best practice is to subscribe whether or not you use Risk Spotter.
Which action must be performed after the Alerter configuration is distributed from the Central Manager to its managed units?
Options:
Unregister the registered managed unit
Reboot the managed unit
Refresh the managed unit
Restart the managed unit portal
Answer:
BExplanation:
"After you distribute the configuration, you might need to either reboot or restart any managed units that you have updated. Alerter: Reboot managed units. If Active on Startup is selected, the alerter starts each time the appliance restarts. GUI restart does not take the Active on Startup value. The alerter must be manually restarted on the managed units through the admin portal (Admin Console > Alerter). Since you cannot restart the alerter from the central manager, restart the managed units from the Admin Console for the same effect."
Alerter configuration is read when the Alerter process starts. Distribution only places the new settings on the managed unit. A reboot restarts the Alerter, and with Active on Startup selected it comes back up using the new values.
Restart Portal: Distribute Configurations does not restart the managed units. The Restart Portal action restarts the web portal and does not apply the Alerter's Active-on-Startup behavior, so (D) is not the documented action.
Other services: Anomaly Detection and Session Inference need a restart of the managed units. Results Export, System Backup, Data Archive, Result Archive and Data Export are applied automatically.
Unregistering: Unregistering a unit (A) would remove it from central management.
Which GIM parameter governs GIM's ability to automatically upgrade all bundles?
Options:
auto_install_on_db_server_os_upgrade
gim_listener_default_shared_secret
gim_listener_default_port
auto_upgrade_bundles
Answer:
AExplanation:
"The GIM parameter auto_install_on_db_server_os_upgrade controls GIM's ability to auto-upgrade all bundles. If enabled, when the database server boots up after an operating system upgrade, GIM automatically downloads and install these bundles. This parameter is disabled by default, to prevent unintentional bundle upgrades. It's easiest to enable the parameter before upgrading the database operating system."
It is tied to the database server's boot after an OS upgrade, which is when kernel-dependent components such as K-TAP most often need to be rebuilt or replaced.
Default: Disabled, so bundle upgrades never happen unintentionally.
Other parameters: gim_listener_default_shared_secret and gim_listener_default_port concern listener-mode client registration and authentication. They have no role in upgrades. auto_upgrade_bundles does not exist.
Recommended practice: Enable it before the OS upgrade, and run the S-TAP Agent Upgrade Pre-Check report from the Central Manager.
Which task can be performed with the Investigation Dashboard?
Options:
Creating, saving, and exporting investigation dashboards for forensic analysis.
Modifying Guardium's core analytics engine settings to enhance real-time processing.
Deleting Guardium audit logs to improve performance.
Disabling automatic recovery of critical security alerts.
Answer:
AExplanation:
"Any investigation dashboards, including threat diagnostics, can be encrypted and exported for sharing. Only the dashboard definitions are exported, not the filters. … If you have a dashboard that is configured with a good set of charts for investigating particular incident types, you can share this knowledge with other Guardium users without including actual attack data or revealing the filters."
The Investigation Dashboard is an analyst workspace. Investigators filter and chart activity data, save the views, and export them for reuse. That is a forensic task.
Filter sets: Filters can be private or shared. A knowledgeable administrator can build filters for a particular investigator and share them with that role.
Predefined dashboards: These cannot be saved under their original names.
Visibility: All saved investigation dashboards are public to every user who has dashboard access. A saved default dashboard is seen by everyone.
Other options: The dashboard does not expose engine tuning (B) or delete audit data (C).
Automatic recovery: The recovery monitor is enabled by default and runs every 20 minutes on the Central Manager. It reports in the deployment health views, so (D) is not a dashboard task.
Which action is performed after changing a rule in a policy?
Options:
Restart the inspection engines
Reinstall the policy
Restart the collector
Reinstall the rule
Answer:
BExplanation:
"After you make a change to a policy (such as changes to group members, policy rules, or actions), you must reinstall the policy. You can either reinstall the policy on a managed unit, or select Policy installation schedule from the configuration profile, which allows you to schedule a distribution that pushes the policy from the central manager to specified managed units."
An installed policy is a snapshot loaded into the analysis engine. Editing the definition does not alter the loaded copy until the policy is installed again.
Not needed: Inspection engines and the collector do not need restarting. Policy installation is a runtime operation.
Central management: The Central Manager can push policy to managed units, either on demand or through a distribution schedule in a configuration profile.
Install actions: Install and Override, Install First and Install Last decide where the policy sits among the installed policies
Rules and groups: A change to group membership has the same requirement. The Risk Spotter daily process, for example, updates its risky-users group and reinstalls the policy itself.
Option D: Individual rules are not installed on their own through the GUI. The unit of installation is the policy.
What must be enabled to use the deployment health views?
Options:
Data imports and exports
Alerts in Policy actions
Unit utilization data
Enterprise S-TAP view report
Answer:
CExplanation:
"To use the deployment health views, enable the collection of unit utilization data, configure correlation alerts, and configure data import and export for your environment." Also: "The deployment health views present data gathered from an entire Guardium environment and are only available from a central manager."
Of the listed options, collection of unit utilization data is the item the procedure says to enable. It feeds the CPU, memory and buffer metrics behind the topology, table and dashboard views. Data import and export (A) is configured, not enabled, and correlation alerts are built in Alert Builder, not in policy actions (B).
Where to look: Manage > System View > Deployment Health Topology, Deployment Health Table and Deployment Health Dashboard.
Alerts on the dashboard: Select "View in deployment health dashboard" in the alert definition. The alert must have severity LOW, MED or HIGH to appear.
Missing data: If you see messages such as "Unit utilization report not scheduled" or "Export not scheduled," revisit the configuration procedure.
S-TAP verification: Configure it for all supported S-TAPs so connectivity and inspection-engine data appear.
Cross-CM health view: For several Central Managers, use the cross-CM health view unit type.
What does an accumulation interval mean in Correlation Alerts?
Options:
How often to send notifications from an alert.
How many events to accumulate before sending an alert.
How many alerts to accumulate before sending notification.
How far back to run the query in the alert definition.
Answer:
DExplanation:
"Accumulation Interval – Enter the length of the time interval (in minutes) that the query examines the audit repository, counting back from the current time (for example, enter 10 to examine the last 10 minutes of data)."
A correlation alert runs a query against the audit repository on a schedule. The accumulation interval is the look-back window of that query, so it is a time window and not an event or alert count. Options A and C describe notification behavior, which is controlled by the separate notification frequency. Option B is a threshold concept, which is defined under Alert Threshold.
Move interval window earlier by: This field shifts the window back in time. Big-data (GBDI) data is not available immediately, so about 120 minutes is usually enough to make sure the whole window has data.
Empty windows: If no data falls in the window and the threshold is evaluated per report, the value is 0 and an alert can still fire. If it is evaluated per line, no alert fires.
Aggregators: Alerts that run on aggregators only consider data inside the defined merge period.
Query requirement: The query must contain a timestamp (date) field.
Worked example: For the predefined No Traffic alert, a 60-minute accumulation interval means "no traffic from this server in the last hour, but some traffic in the last 48 hours."
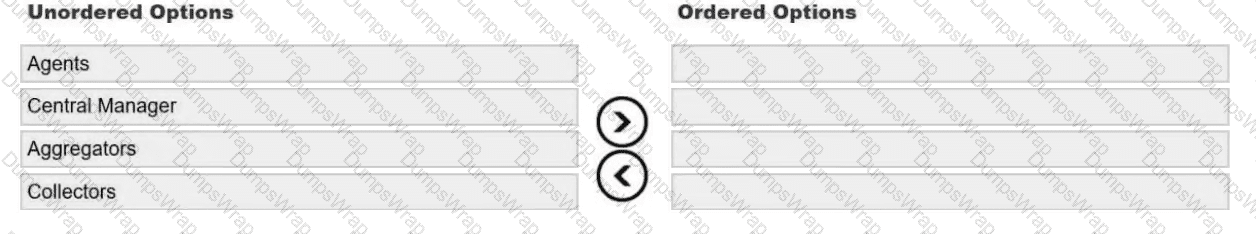
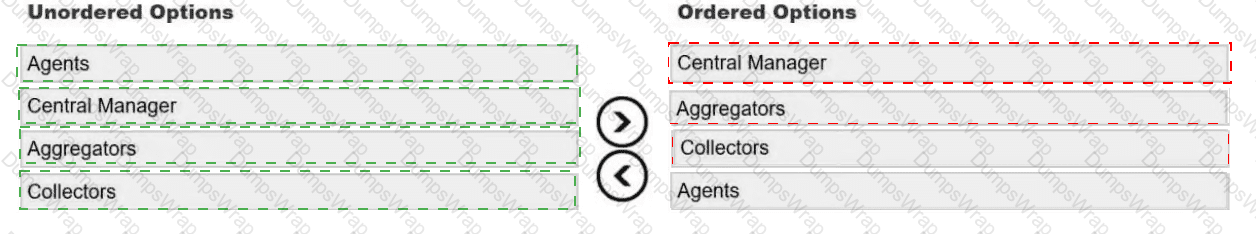
What sequence should be followed to successfully upgrade an environment with 1 Central Manager, 2 Aggregators, and 4 Collectors?
Options:
Answer:
Explanation:
1. Central Manager
2. Aggregators
3. Collectors
4. Agents
Guardium upgrades follow a top-down approach: "A top-down approach is necessary because an upgraded aggregator can aggregate data from older releases, but an older aggregator cannot aggregate data from collectors on newer releases. Similarly, an upgraded central manager can manage units running older releases, but the managed units are not fully functional until they are upgraded to match the central manager. … upgrade a central manager before upgrading any of its managed units … upgrade an aggregator before upgrading any units that export data to it … Finally, upgrade a collector before upgrading the S-TAPs registered to it."
The order follows the direction of data flow and control. Agents (S-TAPs) send traffic to collectors, collectors export to aggregators, and the Central Manager sits above all of them. Each tier must be able to accept data from, or manage, the tier below it at an older level. It cannot accept data from a tier that is newer than itself.
Mixed-version state: The environment stays mixed-version while the upgrade is in progress. Data collection, assessment and policies keep working, but new functionality is limited and you should not make configuration changes.
Failover collectors: Use failover collectors so S-TAP data collection is not interrupted while a collector is being upgraded.
TLS 1.2: Guardium 12.0 requires TLS 1.2 or later. Managed units and S-TAPs that cannot negotiate it are disconnected after the upgrade.
Branch by branch: With several aggregators, upgrade one aggregator and its collectors, then their S-TAPs, before moving to the next branch.
Patch level: After each unit is patched, confirm the level with show system patch installed . If the Central Manager does not show the new version of an upgraded unit, refresh the managed-unit list.
After identifying the traffic that must be monitored, which action limits logging?
Options:
Checking the Selective audit trail option on the Policy Editor
Selecting the role review-only to filter the data
Categorizing the policy as Audit Mode
Entering an Audit pattern to process the data
Answer:
AExplanation:
"Use the selective audit trail option to limit the amount of logging on the Guardium system. … Without a selective audit trail policy, the Guardium appliance logs all traffic that is accepted by the inspection engines. … When a selective audit trail policy is installed, only the traffic requested by the policy is logged."
Selective audit trail is the policy-level switch that changes the logging behavior from "log everything the inspection engines accept" to "log only what the policy asks for."
Audit pattern: An audit pattern in the Policy Definition panel is a regular-expression string match applied to each SQL statement. It does not match session variables such as the database name. This is option D. It is a refinement that only works under a selective audit trail policy, so it is not the action that turns limiting on.
Audit Only or Log actions: Use Audit Only or a Log action on the rules, which can match exact values, groups and patterns.
When to use it: It suits cases where the traffic of interest is a small share of what the inspection engines accept, or where everything you may ever need to report on can be identified in advance.
Other options: The review-only role restricts what a user can view and has no effect on logging. "Audit Mode" is not a policy category.
Complement: To reduce traffic before it reaches the collector, ignore trusted connections or specific IPs at the S-TAP.
Which action ensures that the 'Data Archive' page keeps data for only 7 days?
Options:
Archive and Purge options checked with 'Data older than 1 day' and scheduled to run daily.
Purge checked with 'Data older than' set to 7 days and set to run once a week.
Archive checked with 'Archive Data older than' set to 7 days and scheduled to run daily.
Purge checked with 'Data older than' set to 7 days and scheduled to run daily.
Answer:
DExplanation:
"Archive preserves information for future use. Purge frees up space and speeds up access operations on the internal database. … If both archive and purge are scheduled, purge runs after archive. The export, archive, and purge functions can work on the same data, but not the same date ranges. For example, you may want to export and archive all information older than one day and purge all information older than one month, thereby always leaving one month of data on the sending unit."
Retention is controlled by purge, not archive. Purging data older than 7 days on a daily run means the oldest data on the unit is never more than about seven days old.
A: This keeps about one day, not seven.
B: A weekly run lets data accumulate to as much as 14 days before purging.
C: Archive copies data to external storage. It does not remove anything from the appliance.
Archive settings: "Archive data older than" and "Ignore data older than" define the archive window. Archive daily and purge after 30 days, and each day is archived 30 times.
Verification: Check Manage > Reports > Data Management > Aggregation/Archive Log. Every activity should show Succeeded.
Aggregator tip: Keep the purge period to a maximum of 90 days, with no more than 10 collectors per aggregator.
