
GitHub Actions Exam Questions and Answers
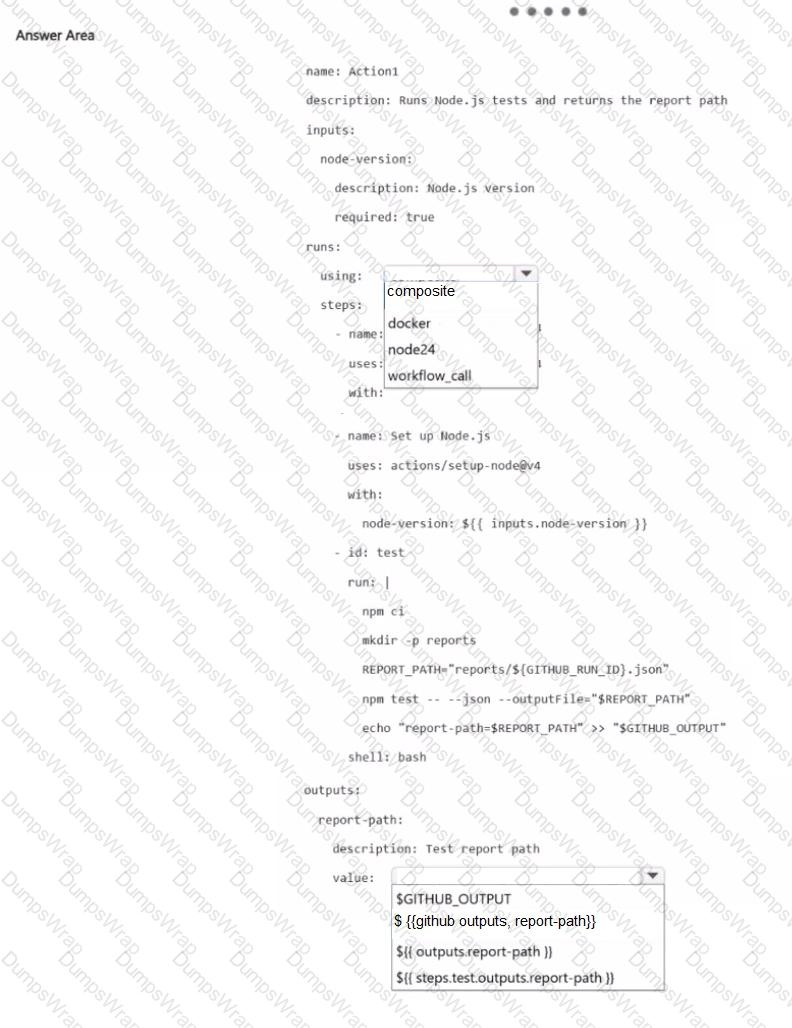
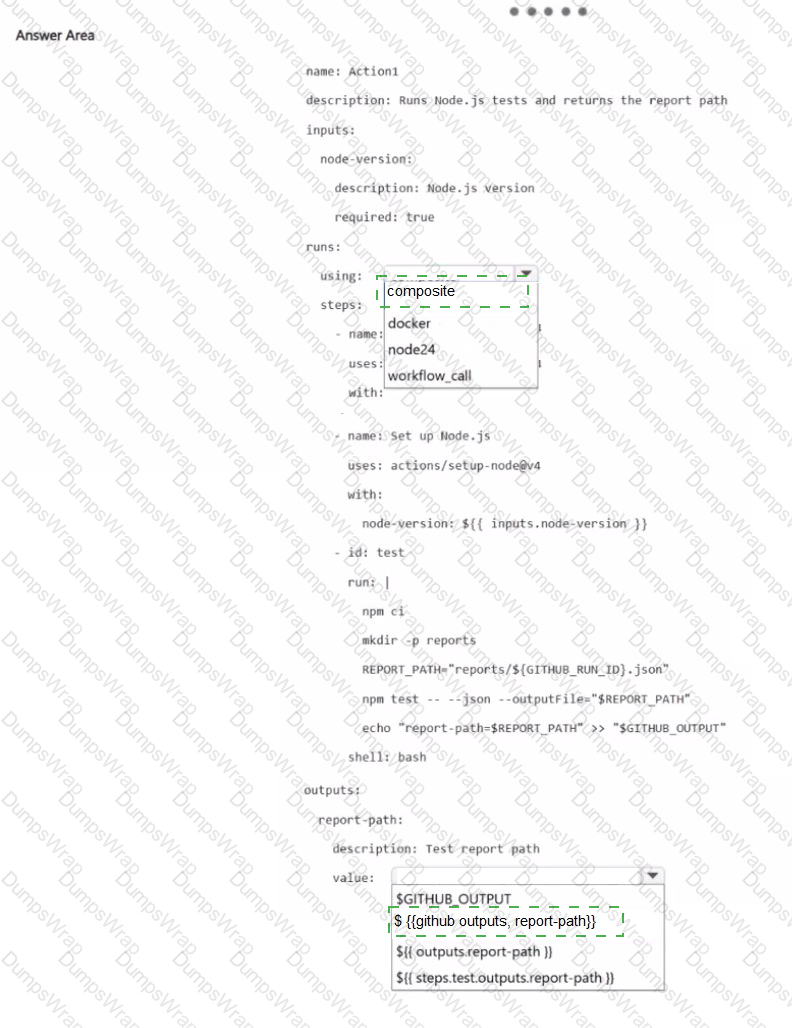
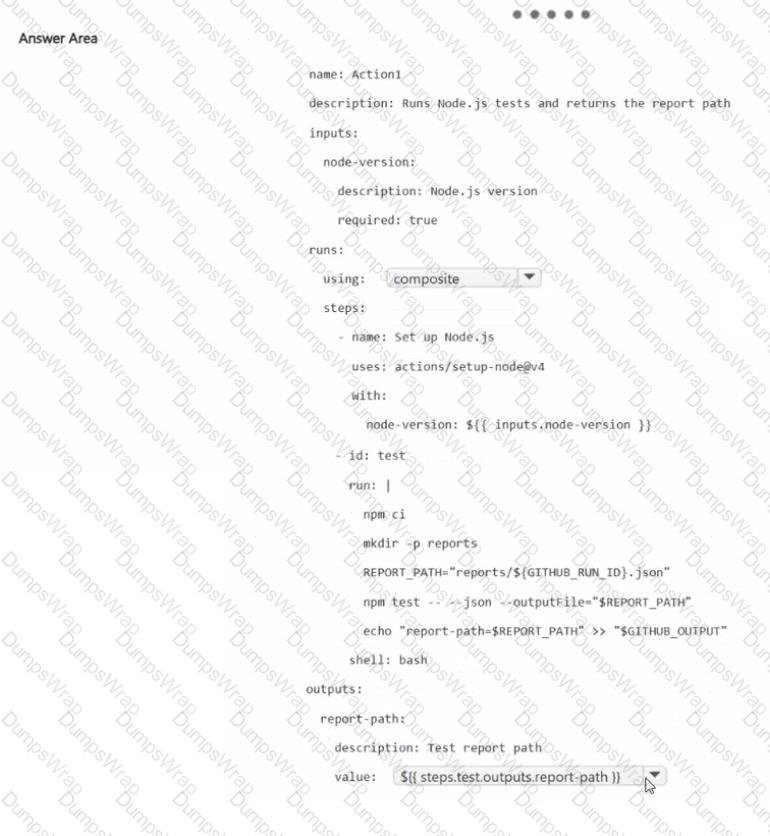
You have a GitHub repository that contains a Node.js project and a local action named Action1. Multiple jobs in repository workflows call Action1. Action1 installs dependencies, runs tests, and returns a generated report path to the calling workflows.
You need to ensure that Action1 meets the following requirements:
• Encapsulates multiple workflow steps without packaging a separate runtime
• Exposes the report path produced by the test step
How should you complete the metadata file? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
As a developer, your self-hosted runner sometimes looses connection while running jobs. How should you troubleshoot the issue affecting your self-hosted runner?
As a developer, you want to review the step that caused a workflow failure and the failed step ' s build logs. First navigate to the main page of the repository on GitHub. Which section contains the step failure information?
How can GitHub Actions encrypted secrets be used in if: conditionals within a workflow job?
As a DevOps engineer, you are trying to leverage an organization secret in a repo. The value received in the workflow is not the same as that set in the secret. What is the most likely reason for the difference?
Which workflows can use an action stored in an internal repository when repository access is enabled for the organization or enterprise?
(Each correct answer presents a complete solution. Choose two.)
What are the two most significant advantages of adding documentation while distributing custom actions? Each correct answer presents a complete solution.
NOTE: Each correct answer is worth one point.
Where should workflow files be stored to be triggered by events in a repository?
You are reaching your organization ' s storage limit for GitHub artifacts and packages. What should you do to prevent the storage limit from being reached?
As a developer, how can you identify a JavaScript action on GitHub?
Your organization is managing secrets using GitHub encrypted secrets, including a secret named SuperSecret. As a developer, you need to create a version of that secret that contains a different value for use in a workflow that is scoped to a specific repository named MyRepo. How should you store the secret to access your specific version within your workflow?
You need to use a specific version of an action. How should you use v1 of an actions/javascript-action repository in your workflow?
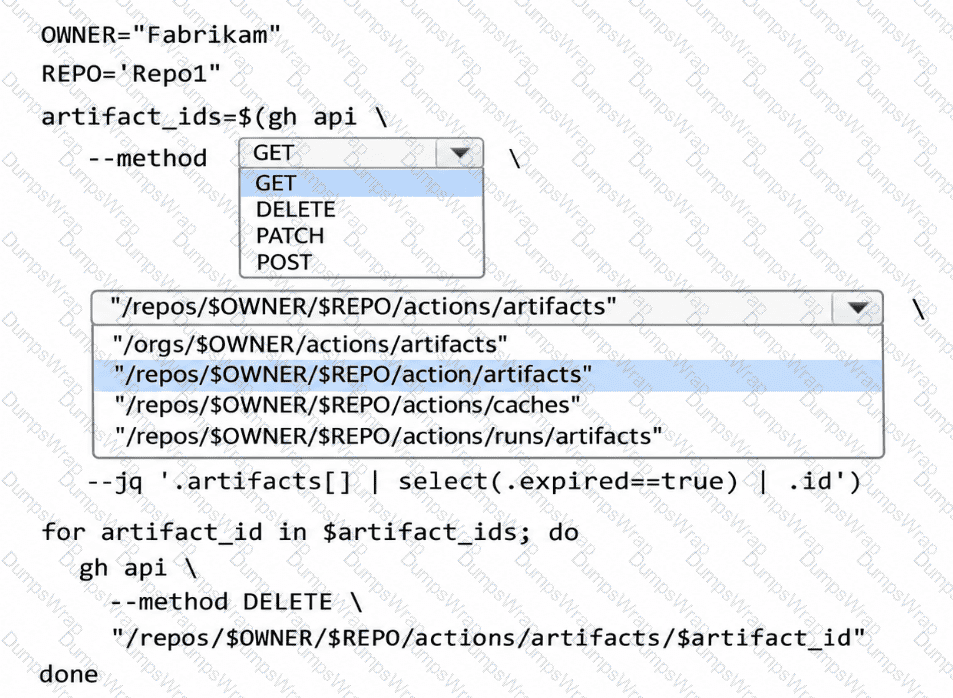
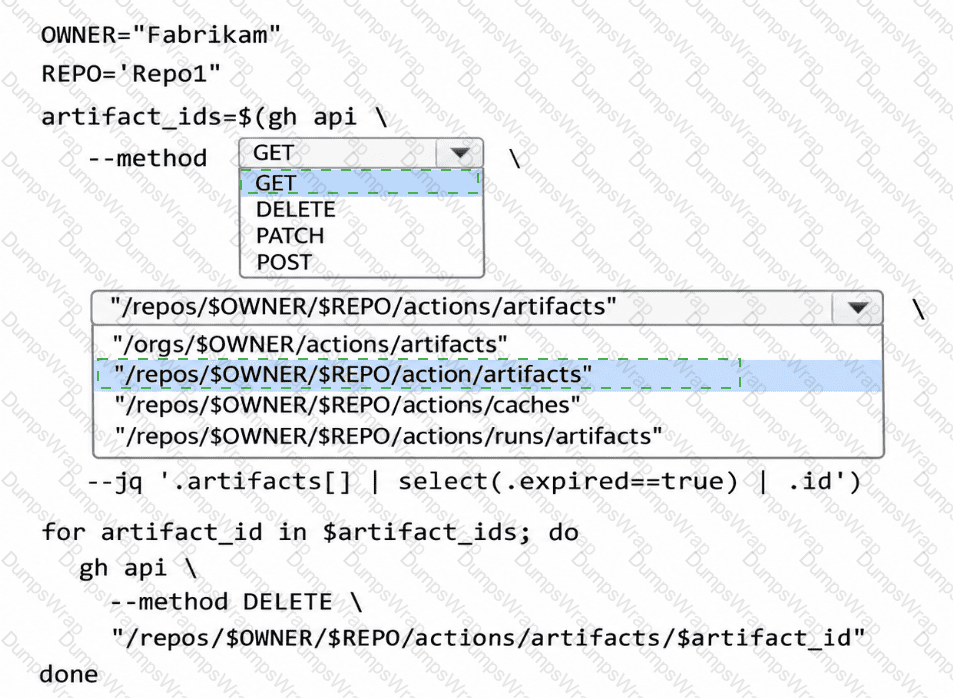
You have a GitHub repository named Repo1. Repo1 uses GitHub Actions workflows that upload build artifacts
You plan to change the artifact and log retention period to 30 days.
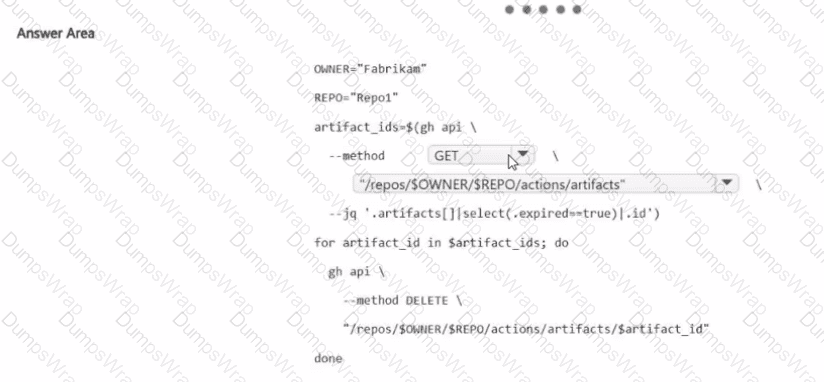
You need to remove expired GitHub Actions artifacts from Report. The solution must explicitly identify and delete existing expired artifacts by using the REST API.
How should you complete the script? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
As a developer, which of the following snippets will enable you to run the commands npm ci and npm run build as part of a workflow?
Which of the following is a valid reusable workflow reference?
You need to create a reusable GitHub Actions workflow template named ci.yml. The solution must ensure that ci.yml appears on the New workflow interface of GitHub Actions. Where should you store ci.yml?
What is the right method to ensure users approve a workflow before the next step proceeds?
You are a developer, and your container jobs are failing on a self-hosted runner. Which requirements must you check to ensure that the self-hosted runner is properly configured? (Choose two.)
Which workflow command would output the debug message " action successfully debugged " ?
What is a valid scenario regarding environment secrets?
Which of the following is the most common way to target a specific major release version?
You are a DevOps engineer working on a custom action. You want to conditionally run a script at the start of the action, before the main entrypoint. Which code block should be used to define the metadata file for your custom action?
As a developer, you are optimizing a GitHub workflow that uses and produces many different files. You need to determine when to use caching versus workflow artifacts. Which two statements are true? (Choose two.)
You are a DevOps engineer working on custom Actions development. You need to handle the errors or exceptions as part of the JavaScript-based action code. What should be added to the following code block to handle errors?
Exhibit:
const core = require( ' @actions/core ' );
try {
// action code
} catch (error) {
< < insert snippet here > >
}
As a developer, you are configuring GitHub Actions to deploy VMs to production. A member of the VMOps team must provide approval before the deployment occurs. Which two steps should you take? Each correct answer presents part of the solution.
NOTE: Each correct answer is worth one point.
As a DevOps engineer, you are developing a composite action. You have a step that needs to be executed against a subdirectory. Which code snippet should you use within the composite action to specify the directory?
In which scenarios could the GITHUB_TOKEN be used? (Choose two.)
You are a DevOps engineer working on a custom action. You want to conditionally run a script at the start of the action, before the main entry point. Which code block should be used to define the metadata file for your custom action?
What are the most significant advantages of adding documentation while distributing custom actions?
(Each answer presents a complete solution. Choose two.)
As a DevOps engineer, you need to define a deployment workflow that runs after the build workflow has successfully completed. Without modifying the build workflow, which trigger should you define in the deployment workflow?
As a developer, you have a 10-MB data set that is required in a specific workflow. Which steps should you perform so the dataset is stored encrypted and can be decrypted during the workflow? (Choose three.)
Which run: command will set a step ' s output?
What are two reasons to keep an action in its own repository instead of bundling it with other application code?
(Each correct answer presents a complete solution. Choose two.)
What are the two ways to pass data between jobs? (Choose two.)
How can a workflow deployment mitigate the risk of multiple workflow runs deploying to a single cloud environment simultaneously?
(Each correct answer presents part of the solution. Choose two.)
How should you print a debug message in your workflow?
As a developer, you need to add the correct syntax to allow the following workflow file to be triggered by multiple types of events.
Which two code blocks should you add starting at line 5? Each correct answer presents a complete solution.
NOTE: Each correct answer is worth one point.
4 name: Node CI/CD
5
6
7
8 jobs:
9 build:
10 runs-on:
11 steps:
12 - uses: actions/checkout@v2
13 - uses: actions/setup-node@v1
14 with:
15 node-version: 12
16 - run: npm ci
17 - run: npm test
18
Custom environment variables can be defined at multiple levels within a workflow file, including which three levels?
(Each correct answer presents a complete solution. Choose three.)
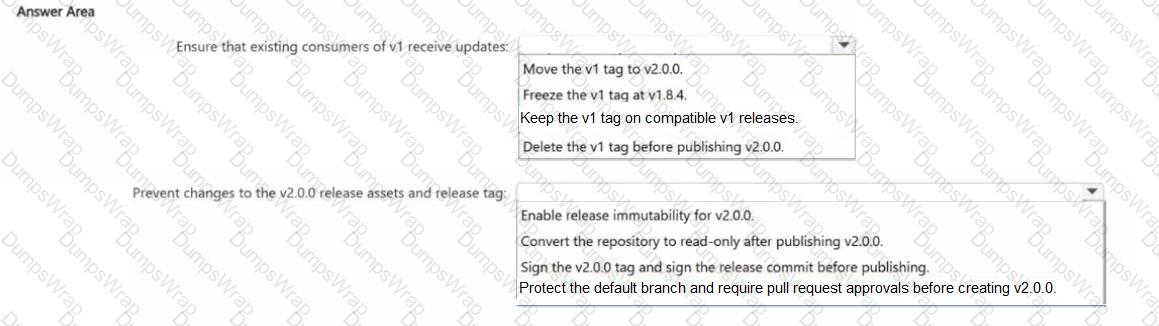
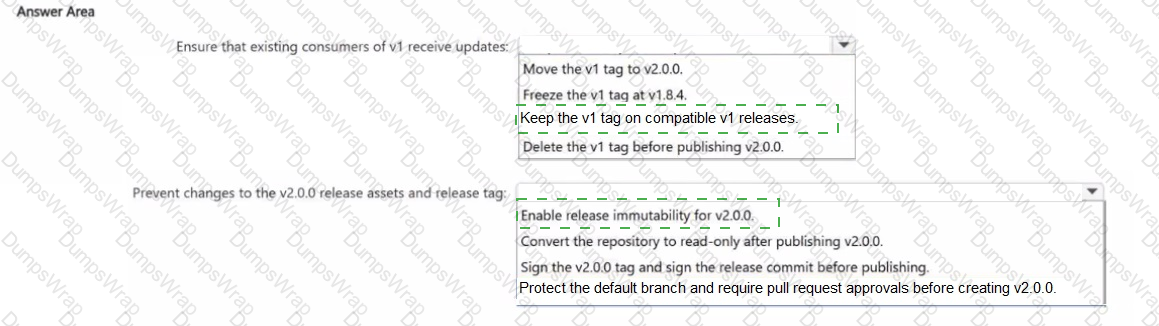
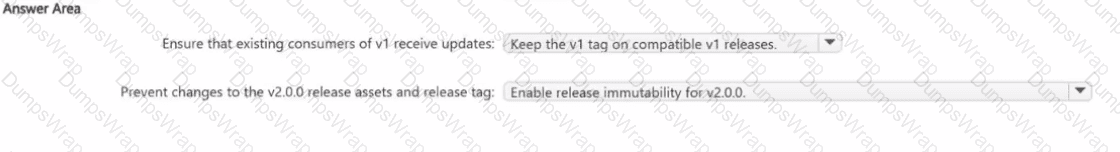
You have a GitHub Enterprise Server instance that hosts a custom action repository named action1. Production workflows use the actions in action1 as action1@vl. The current stable release of action1 is vl.8.4.
You need to publish a new release of action1 with version number v2.0.0 that changes an input name and includes release assets. The solution must meet the following requirements:
• Ensure that existing consumers of v1 continue to receive backward-compatible updates.
• Prevent changes to the published V2.0.0 release assets and release tag after publication.
What should you do for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
What is the most secure way to store sensitive information in GitHub Actions workflows?
Which of the following commands will set the $FOO environment variable within a script, so that it may be used in subsequent workflow job steps?
For which type of GitHub Actions workflows should you use a self hosted runner?
Which of the following is the lowest repository permission you need to have for downloading workflow artifacts?
You create a self-hosted runner labeled as runner1.
You need to ensure that a GitHub Actions workflow job runs only on runner1.
Which YAML statement should you use?
