Microsoft Certified: Cloud and AI Security Engineer Associate Questions and Answers
You need to implement the function apps to meet the technical requirements.
Which apps should you include in the implementation?
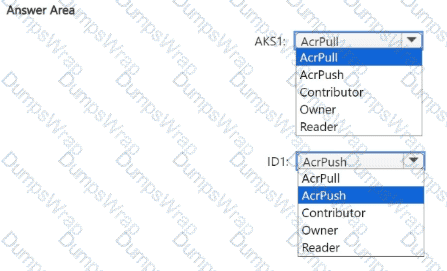
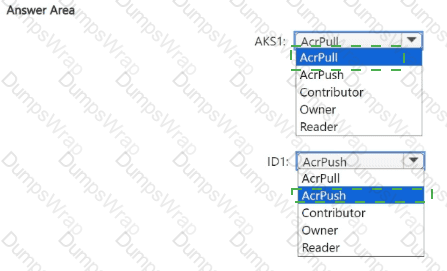
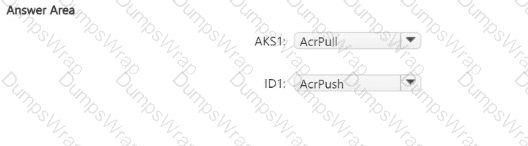
You need to configure the AKS1 and ID1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to implement the planned change for storage2. The solution must meet the technical requirements for storage encryption.
What should you do?
You need to implement the planned change for WAF1. The solution must minimize administrative effort.
What should you do?
You need to delegate a user to implement the planned change for Defender for Cloud. The solution must follow the principle of least privilege.
Which user should you choose?
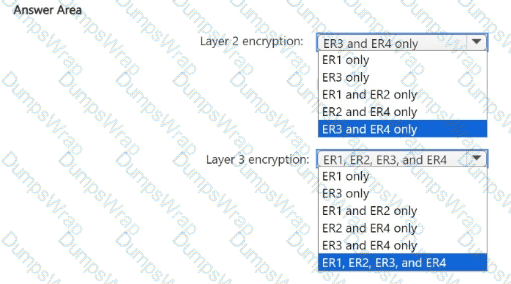
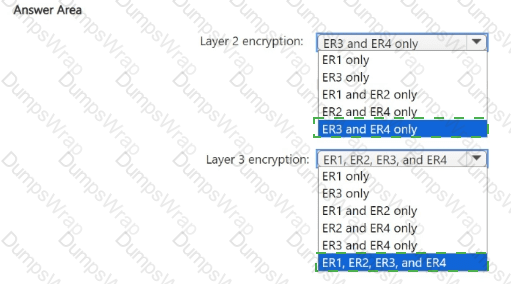
You need to recommend an encryption solution for the planned ExpressRoute implementation. The solution must meet the technical requirements.
Which ExpressRoute circuit should you recommend for each type of encryption? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to implement the planned change for VM1 to access storage1. The solution must meet the technical requirements.
What should you do first?
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 7
You need to collect all the audit failure data from the security log of a virtual machine named VM1 to an Azure Storage account. To complete this task, sign in to the Azure portal.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 1
You need to configure Azure to allow RDP connections from the Internet to a virtual machine named VM1. The solution must minimize the attack surface of VM1.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 10
You need to create a new Azure AD directory named 28681041.onmicrosoft.com. The new directory must contain a new user named user1@28681041.onmicrosoft.com.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 9
You need to ensure that the rg1lod28681041n1 Azure Storage account is encrypted by using a key stored in the KeyVault28681041 Azure key vault.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 3
The developers at your company plan to create a web app named App28681041 and to publish the app to You need to perform the following tasks:
• Ensure that App28681041 is registered to Azure AD.
• Generate a password for App28681041.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 6
You need to email an alert to a user named adminl@contoso.com if the average CPU usage of a virtual machine named VM1 is greater than 70 percent for a period of 15 minutes.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 2
You need to add the network interface of a virtual machine named VM1 to an application security group named ASG1.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 5
You need to ensure that only devices connected to a 131-107.0.0/16 subnet can access data in the rg1lod28681041 Azure Storage account.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 8
You need to prevent HTTP connections to the rg1lod28681041n1 Azure Storage account.
Lab Task
use the following login credentials as needed:
To enter your username, place your cursor in the Sign in box and click on the username below.
To enter your password. place your cursor in the Enter password box and click on the password below.
Azure Username: Userl -28681041@ExamUsers.com
Azure Password: GpOAe4@lDg
If the Azure portal does not load successfully in the browser, press CTRL-K to reload the portal in a new browser tab.
The following information is for technical support purposes only:
Lab Instance: 28681041
Task 4
You need to ensure that a user named user2-28681041 can manage the properties of the virtual machines in the RG1lod28681041 resource group. The solution must use the principle of least privilege.
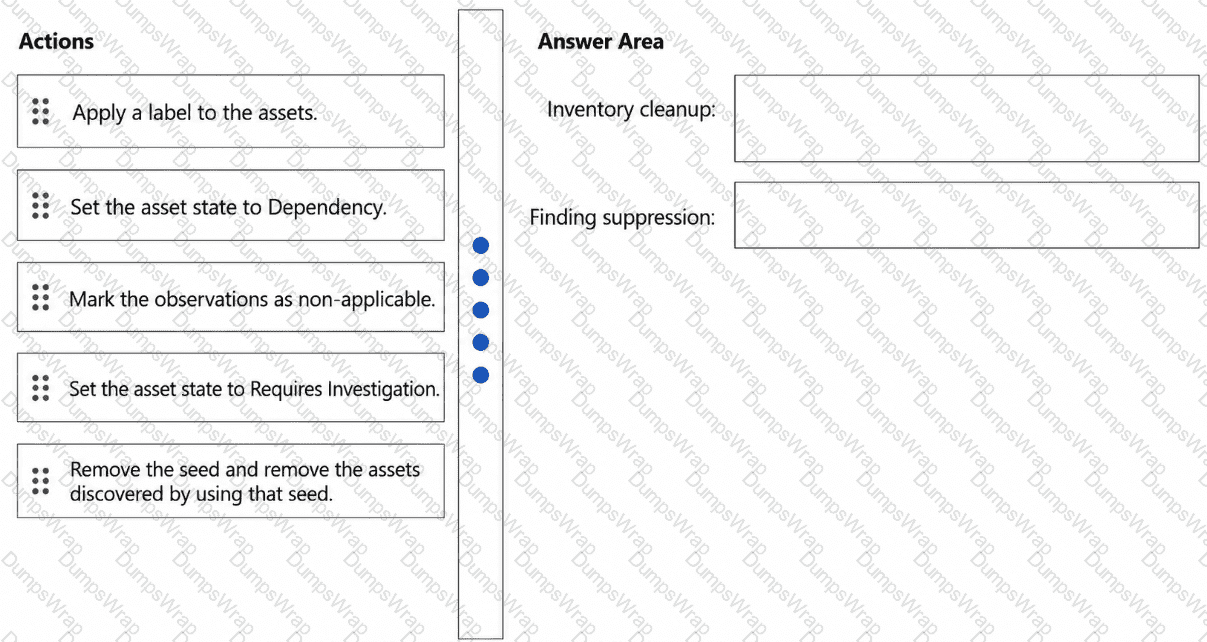
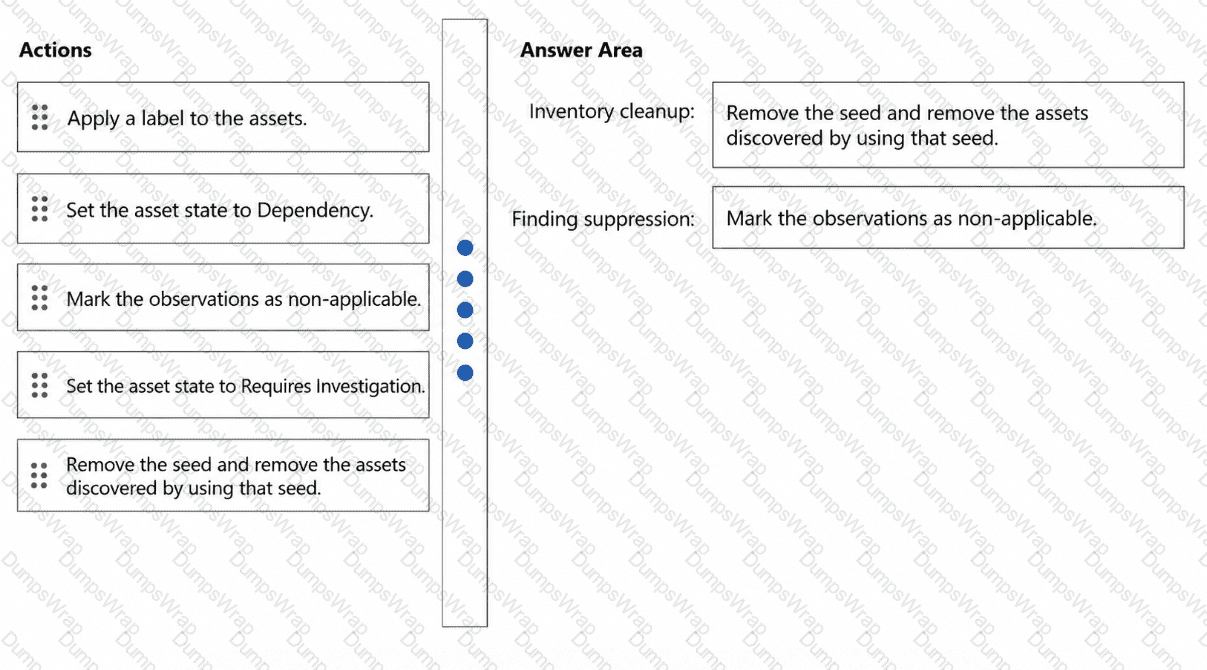
You have a Microsoft Defender External Attack Surface Management (Defender EASM) resource for a company named Contoso. Ltd.
You need to update the Defender EASM workflow to meet the following requirements:
•Assets from a business domain that Contoso no longer owns must be removed from inventory.
•Findings that do NOT apply to confirmed inventory must NOT affect reported counts.
What should you do for each requirement? To answer, drag the appropriate actions to the correct requirements. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

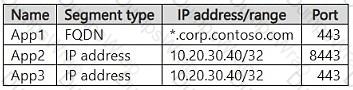
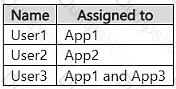
You have three on-premises apps named App1, App2, and App3 that are configured in Microsoft Entra Private Access as shown in the following table.
You have the users shown in the following table.
The Global Secure Access client is deployed to all user devices.
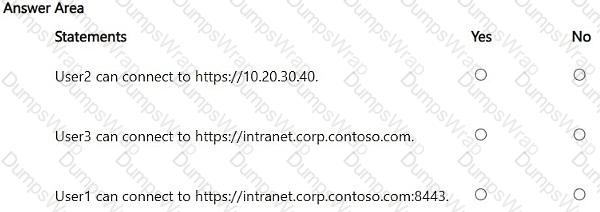
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

You have an Azure virtual network named VNet1 that contains a subnet named Subnet1.
You create a storage account named storage1.
You need to ensure that access to storage1 can be managed only by a network security group (NSG) linked to Subnet1.
What should you use?
HOTSPOT
You have an Azure subscription that contains a virtual network named VNet1 with the following subnets:
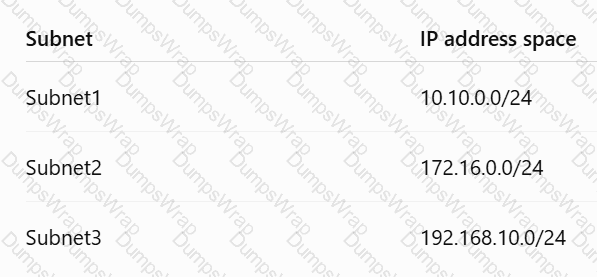
The subscription contains:
VM1 → Subnet1
VM2 → Subnet2
VM3 → Subnet3
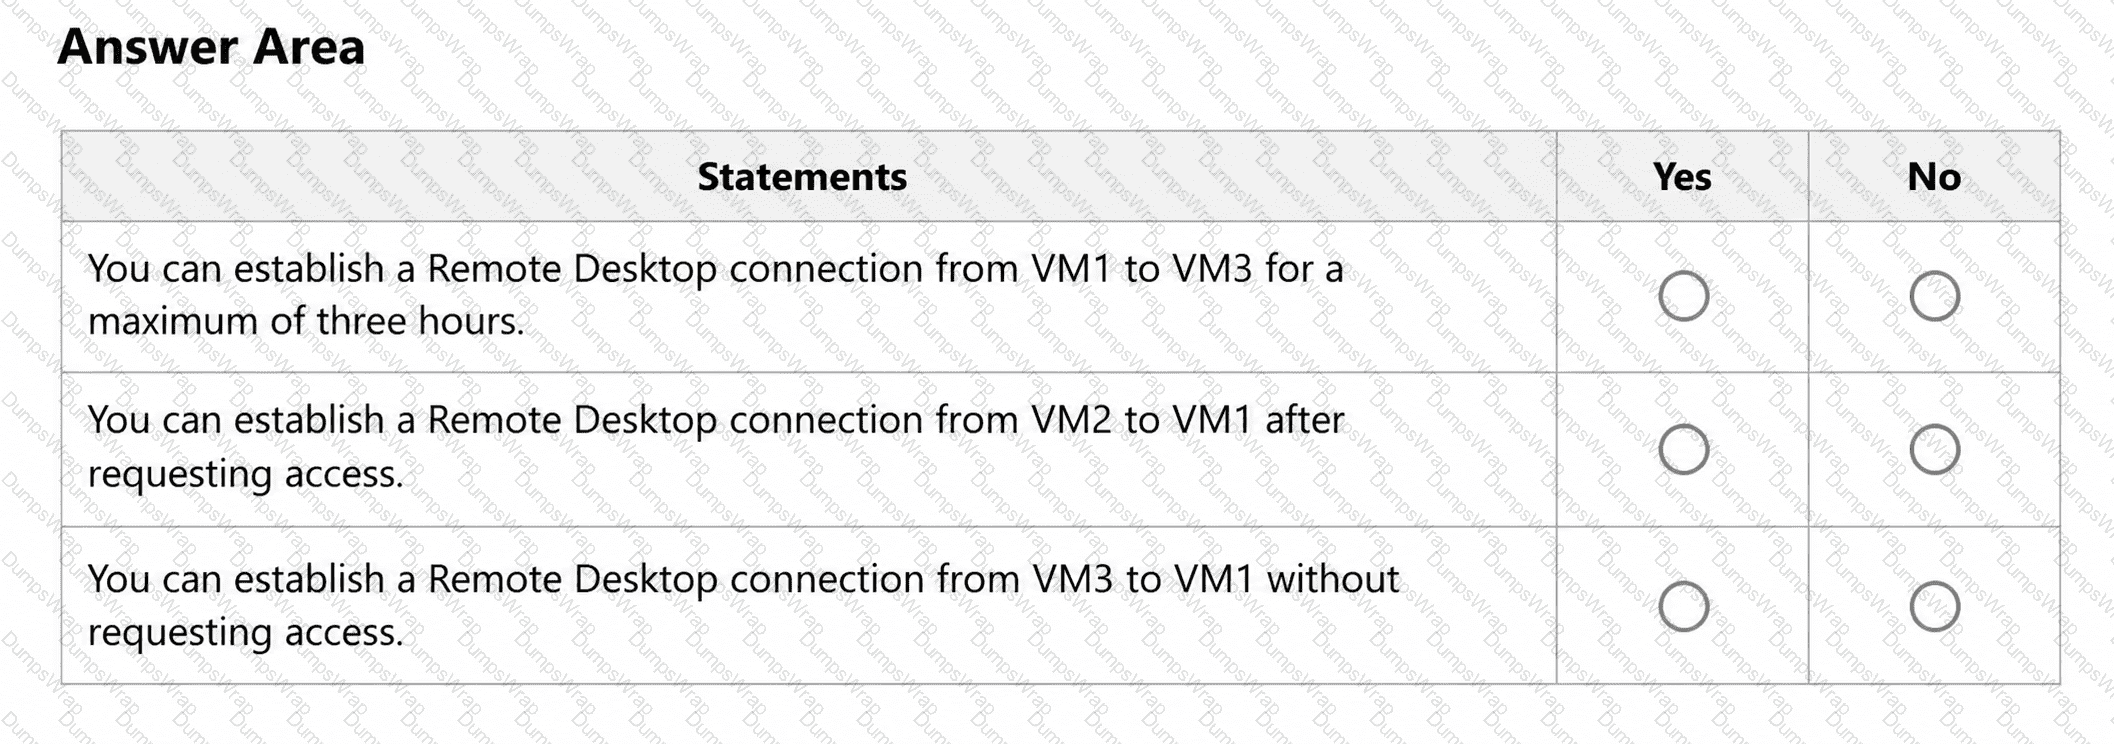
VM3 contains a service that listens on port 8080.
For VM1, you configure Just-in-Time (JIT) VM access:
Port 3389: allowed source IPs 10.10.0.0/24, 192.168.10.0/24, maximum 3 hours
Port 8080: source IPs Per request, maximum 5 hours
For each statement, select Yes if the statement is true. Otherwise, select No.

You have an Azure subscription that contains an Azure SQL Database logical server named SQL1 and an Azure virtual machine named VM1. VM1 uses a private IP address only. The Firewall and virtual networks settings for SQL1 are shown in the following exhibit.
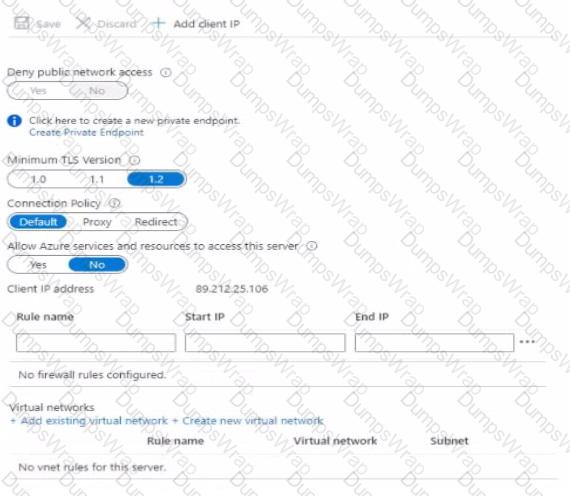
You need to ensure that VM1 can connect to SQL1. The solution must use the principle of least privilege.
What should you do on the SQL1 Firewall and virtual network settings?
You have an Azure subscription that contains an Azure SQL database named SQL1.
You plan to deploy an Azure app service web app named Appl.
You need to provide App1 with read and write access to SQL1. The solution must meet the following requirements:
• Provide App1 with access to SQL1 without storing a password.
• Use the principle of least privilege.
• Minimize administrative effort.
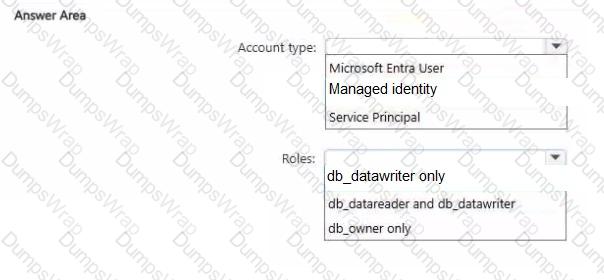
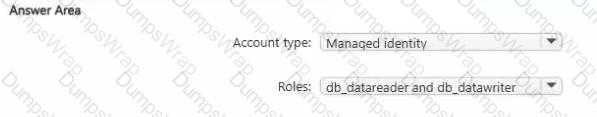
Which type of account should App1 use to access SQL1, and which database roles should you assign to App1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

You have an Azure subscription that contains a key vault and an Azure SQL server.
You need to deploy an Azure SQL database that uses Transparent Data Encryption (TDE) and a customer-managed key.
What should you create before you deploy the database?
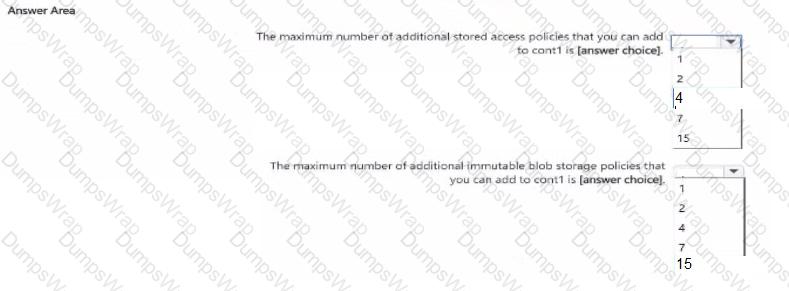
You have an Azure subscription that contains a blob container named cont1. Con1 ' has the access policies shown in the following exhibit.
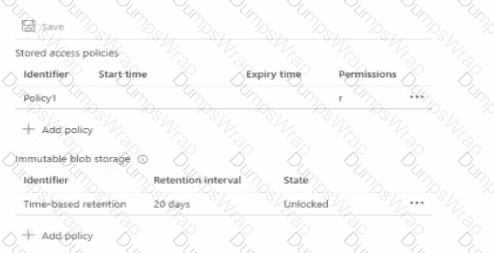
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

You have Microsoft Security Copilot agents that authenticate by using Microsoft Entra service principals.
You receive a Microsoft Defender alert triggered by the anomalous OAuth authentication of an agent ' s Microsoft Entra service principal.
You need to assess the impact of the agent identity and identify which resources are affected if the identity is abused for lateral movement. The solution must minimize administrative effort.
What should you do?
HOTSPOT
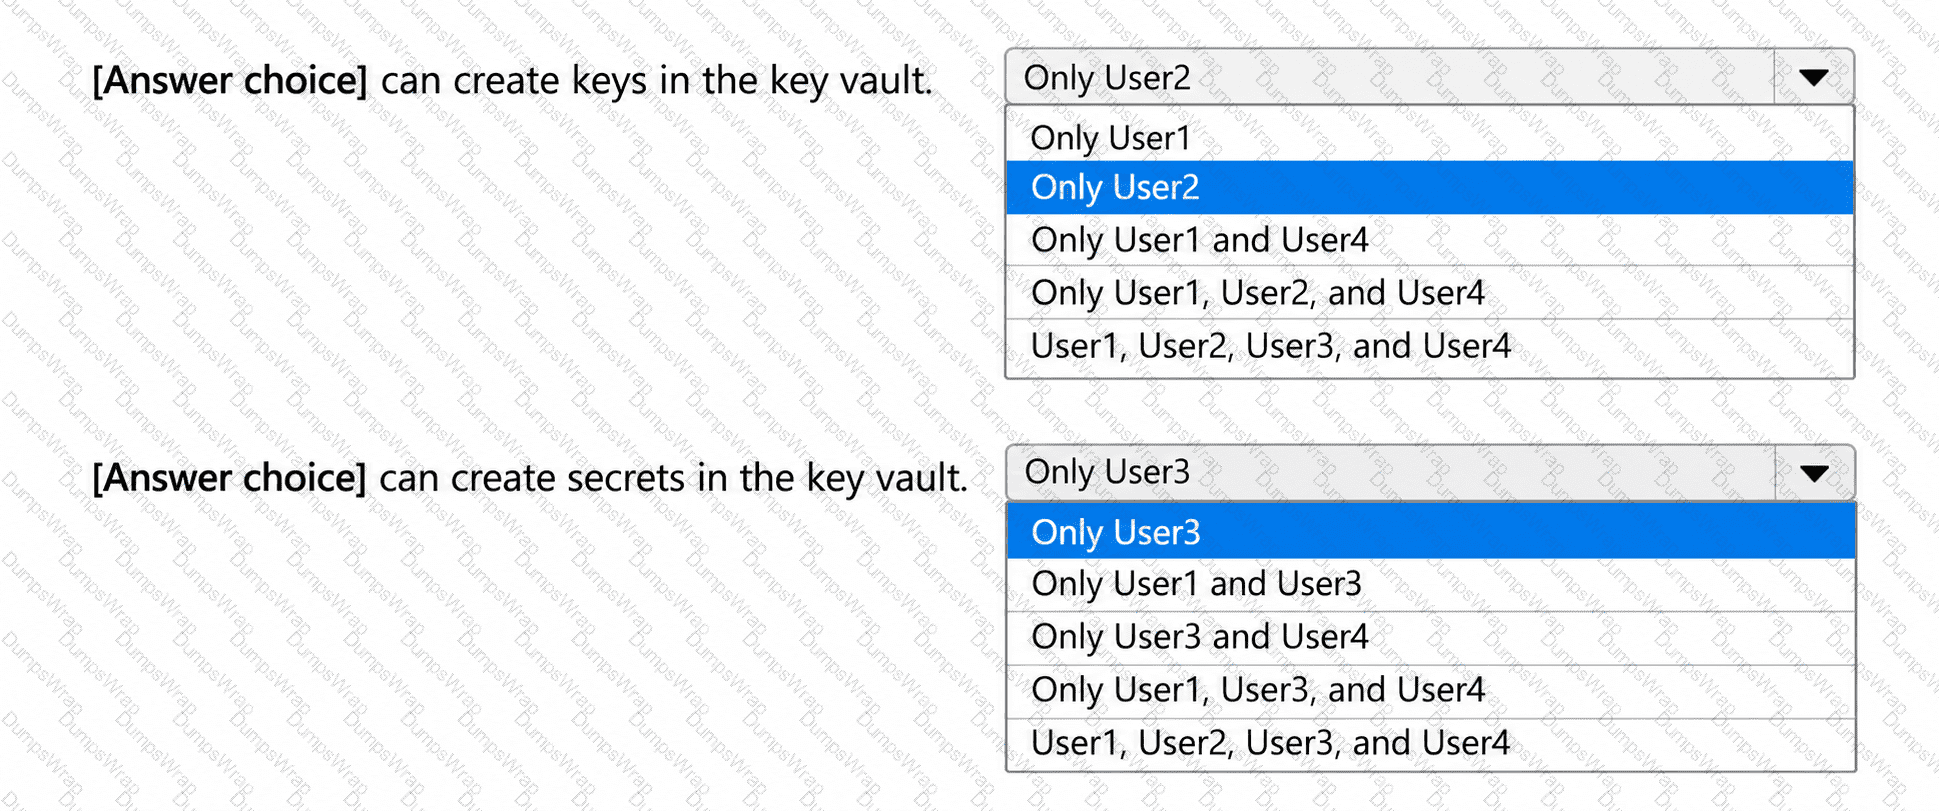
You have an Azure subscription that contains an Azure key vault named KeyVault1.
The role assignments are:
User1 → Owner, scoped to the subscription
User2 → Key Vault Crypto Officer, scoped to KeyVault1
User3 → Key Vault Secrets Officer, scoped to KeyVault1
User4 → Key Vault Administrator, scoped only to KeyVault1/keys/Key1
Use the drop-down menus to complete each statement.

You have an Azure subscription that has the Microsoft Defender for Cloud Foundational Cloud Security Posture Management (CSPM) plan enabled.
You have an Amazon Web Services (AWS) account connected to Defender for Cloud for posture management.
In Defender for Cloud, security recommendations for the resources in Azure and AWS have a risk level of Not evaluated.
You need to ensure that Defender for Cloud assigns a risk level to the recommendations.
What should you do?
You have an Azure subscription named Sub1 that contains a resource group named RG1.
RG1 contains a virtual network named VNet1 and a storage account named storage1. Several engineers are assigned the Owner role for Sub1.
You need to prevent updates to and deletions from VNet1. The solution must ensure that engineers can continue updating other resources in RG1.
Which lock should you apply?
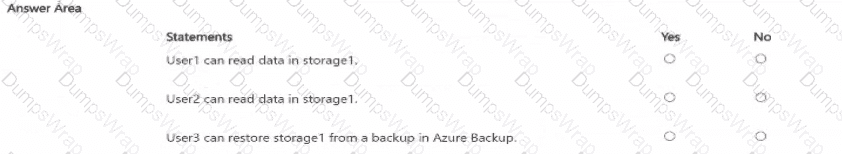
You have an Azure subscription that contains a resource group named RG1. RG1 contains a storage account named storage1. You have two custom Azure roles named Role1 and Role2 that are scoped to RG1. The permissions for Role1 are shown in the following JSON code.


You have a Microsoft Entra tenant that contains a user named Admin1 and is linked to an Azure subscription named Sub1.
Admin1 reports that the Custom recommendation option is unavailable in Microsoft Defender for Cloud as shown in the following exhibit.
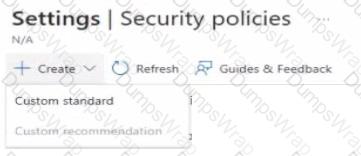
You need to ensure that Admin1 can create a custom recommendation. The solution must follow the principle of least privilege. What should you do?
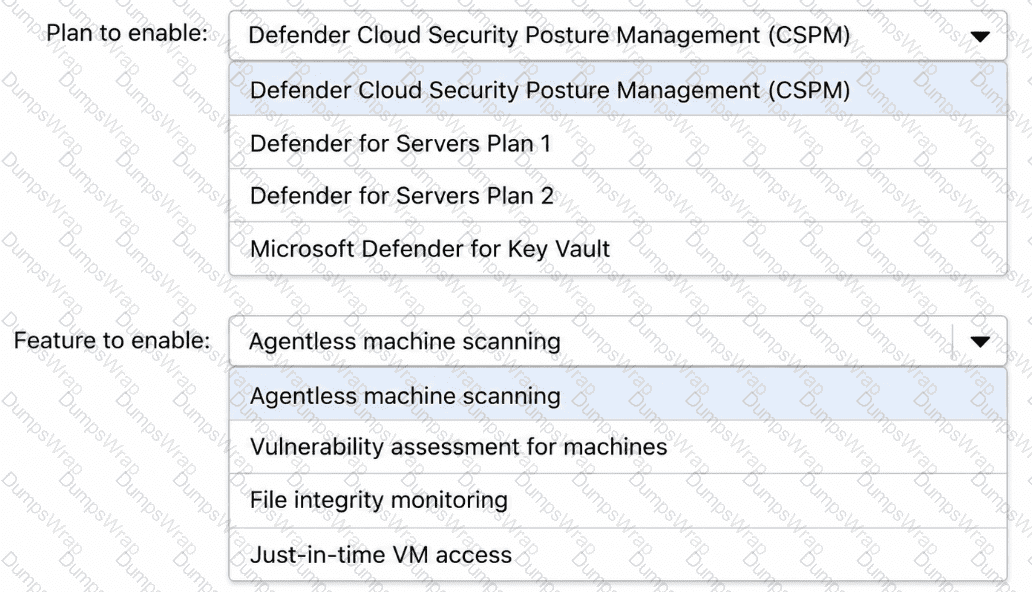
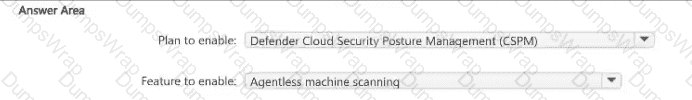
You have an Azure subscription named Sub1 that contains 50 virtual machines. Sub1 has Microsoft Defender for Cloud enabled.
Sub1 contains an Azure key vault named KV1 and an Azure policy that enforces storing all secrets in KV1.
Occasionally, the developers at your company store plaintext tokens and SSH private keys on the virtual machines.
You need to configure Defender for Cloud to detect plaintext secrets on the virtual machines. The solution must minimize administrative changes to the virtual machines.
How should you configure Defender for Cloud? To answer, select the appropriate options in the answer area
NOTE: Each correct selection is worth one point.

You have a Microsoft Entra tenant.
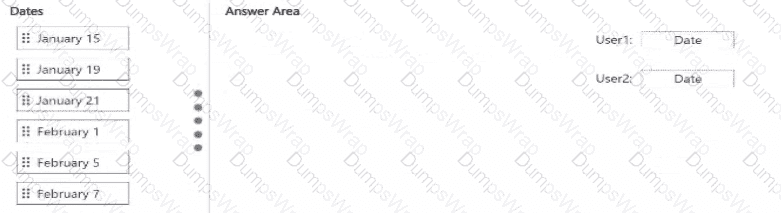
On January 1, you configure a Multifactor authentication registration policy that has the following settings
• Assignments: All users
• Require Microsoft Entra ID multifactor authentication registration: Enabled
• Enforce policy: On
On January 3, you create two new users named User1 and User2.
On January 5, User1 authenticates to Microsoft Entra ID for the first time. On January 7, User2 authenticates to Microsoft Entra ID for the first time.
On which date will User1 and User2 be forced to register for MFA? To answer, drag the appropriate dates to the correct users. Each date may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

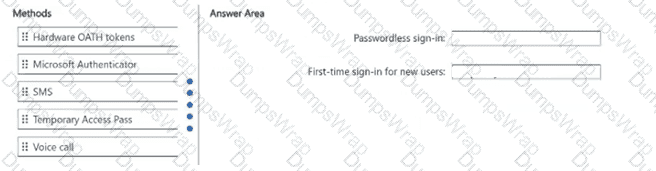
You have a Microsoft Entra tenant.
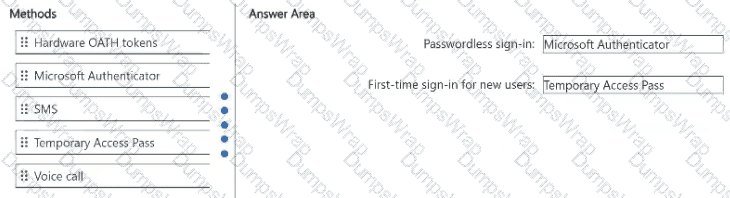
You need to implement password less authentication. The solution must meet the following requirements:
•Users can sign in without a password by using a mobile device.
•New users that sign in for the first time must use a helpdesk issued sign in method that expires.
Which authentication method should you enable for each requirement? To answer, drag the appropriate methods to the correct requirements. Each method may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.